Use case · Privacy by design
Privacy by design at HoundDog.ai means embedding privacy into the way engineers write code. Proactive data minimization, applied as features are built, prevents accidental overlogging and oversharing of sensitive data before it reaches production.
Sensitive data exposures are rarely intentional. They happen as codebases grow. A developer prints a full user object, a tainted variable carries PII through a chain of transformations, and by the time anyone notices, the data has already been logged or sent to a third party.
console.log
Asking questions in plain English
With the self-hosted or cloud platform, your organization’s data map becomes queryable in plain English.
An AppSec engineer asks which sensitive data and auth tokens are leaking into application logs.
Show me all sensitive data and auth tokens leaking in application logs
New chat
Show me all sensitive data and auth tokens leaking in application logs
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
A privacy engineer asks which third-party integrations receive PII.
Which third parties receive PII?
New chat
Which third parties receive PII?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
An AI governance team asks which AI integrations exist and what sensitive data reaches them.
Which AI services receive sensitive data in our code?
New chat
Which AI services receive sensitive data in our code?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
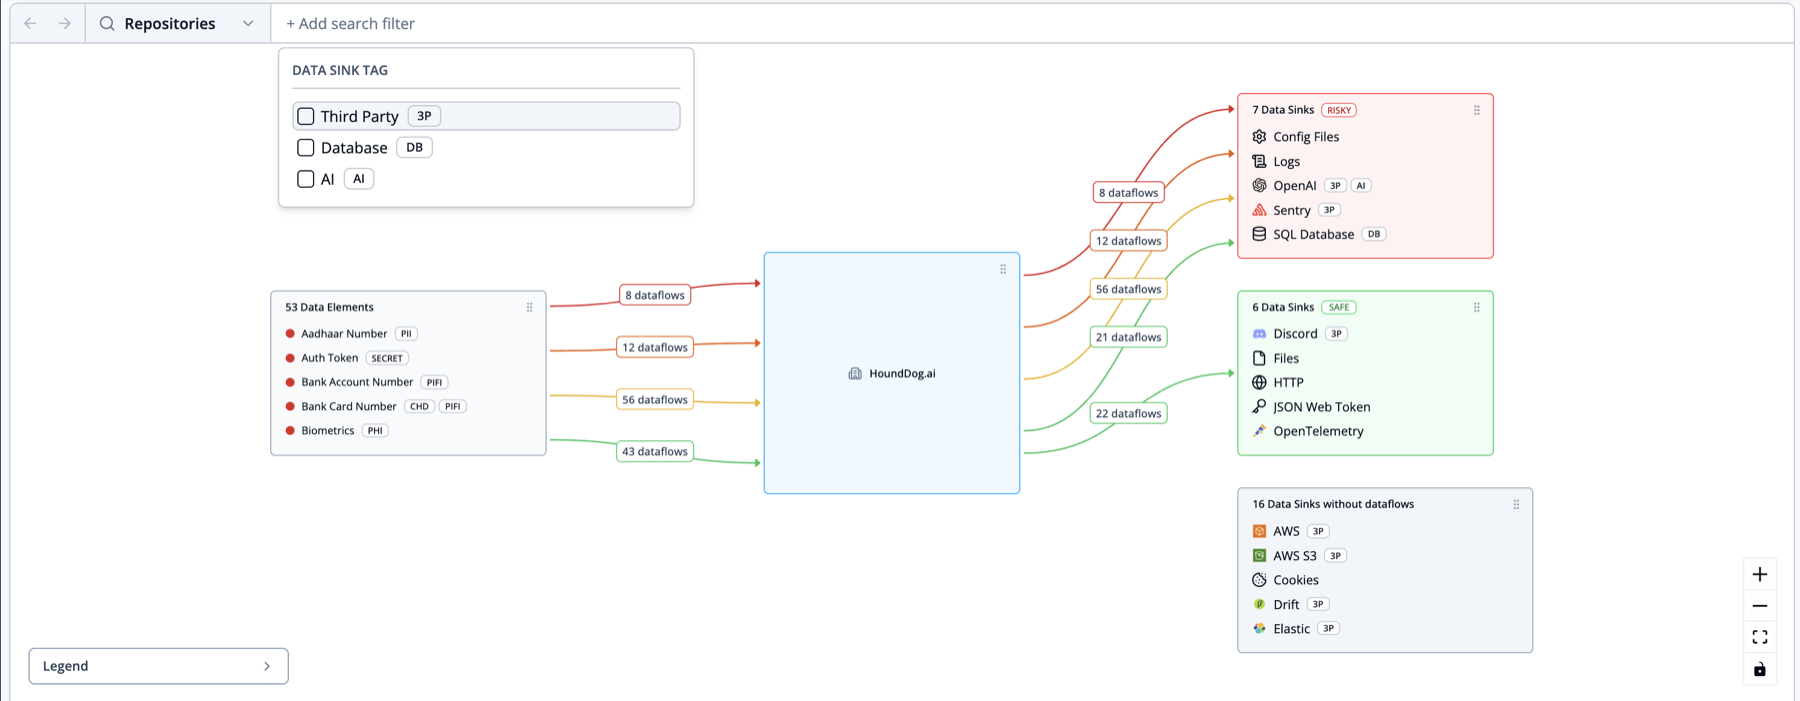
main branch of the hounddogai/hounddog-test-python repository, in one file.Dataflows: one confirmed dataflow, and it is risky.
Without AI, the Datamap is still available, built from the scanner’s deterministic findings. You can apply the same advanced filters to search for dataflows; there is no chat panel and no AI review.
Read the Datamap docs Related: Privacy Code ScanningPII Leak PreventionThird-Party Data Flow MonitoringData Flow Mapping
HoundDog.ai vs. reactive DLP
DLP reacts once sensitive data is already written, and scrubbing it back out is disruptive every time. HoundDog.ai traces the data into the log statement at scan time, before it ever executes.
Example 1 Payment card data in a log statement
HoundDog.ai: caught at scan time
String msg = String.format(
"%s charged %s %s to the %s %s held by %s",
merchant.getName(), amount, currency,
card.getType(), card.getLast4(),
cardholder.getName());
log.warn(msg);
// cardholder + card data traced before it runs
Flagged at scan time. Card data never reaches the log.
Reactive DLP: after the fact
WARN Uber Eats charged 148.27 USD to
the CREDIT VISA-4242
held by Sarah Johnson
([email protected])
Card data already committed. Catching the last four digits depends on context.
Example 2 Auth token in a debug log
HoundDog.ai: caught at scan time
const token = req.headers.authorization;
const user = await auth.verify(token);
console.log("User payload:", user);
// user object contains token + email, traced before it runs
Auth token + email traced and flagged before the log line ever executes.
Reactive DLP: after the fact
DEBUG User payload: {
"email": "[email protected]",
"token": "eyJhbGciOiJIUzI1NiIs...",
"role": "admin"
}
Token already written to stdout. Now in monitoring, SIEM, backups, and analytics.
The business case
Estimate the savings for your own codebase and team.
Go to ROI calculatorBuilt for AppSec, loved by developers
Static analysis discovers. AI reasons. MCP delivers.
HoundDog.ai is built to make your AI more effective, not to replace it.
The scanner discovers every sensitive dataflow, so your AI tokens go to reasoning over detected flows: assessing risk, triaging dataflows and answering questions about your datamap.
The same commit always produces the same dataflows. Every engineer, privacy reviewer and agent gets the same answer about where sensitive data goes, instead of output that varies with the prompt.
The Rust scanner runs in CI on standard CPU infrastructure, across every repo and every commit, with negligible impact on build times.
The leak under the leak
Most PII in logs starts as a debugging shortcut, not a security choice. Understanding the why is half of preventing it. Deeper breakdown in our PII exposure in logs post.
Developers overlog to find root causes faster. Detailed logs pinpoint where a problem started, even in complex systems with subtle errors.
Every logged field is a potential entry point.
The OWASP ASVS and CWE catalog the patterns behind improper log handling.
Less critical apps often have lighter security, making them prime targets if they log PII.
Logs flow everywhere: monitoring, SIEM, backups, analytics.
The cheapest place to secure a log is in the code, before anything ships.
Catch the overlogging and oversharing of sensitive data at the code level, enforce data minimization, and stop risky changes before they reach production. Start free, or book a demo to see it on your own codebase.