Use case · Data security
Modern apps integrate with dozens of third-party SDKs, APIs, and AI services, often added by developers or AI coding assistants without security review. Posture and runtime tools only see leaks after the data has already moved. HoundDog.ai monitors every code change to show which sensitive data elements reach which third parties, including shadow integrations and LLM prompts, before anything ships.
Real examples
User object. Four data exposure paths.Integrations with analytics, observability, CRM, or AI tools often receive contextual data for better insights. Without clear guardrails, developers or AI coding assistants accidentally send full user objects, exposing PII such as names, emails, phone numbers, and even Social Security Numbers, usually by spreading objects into function parameters or logging them unfiltered.
interface User {
id: string;
email: string;
ssn: string;
firstName: string;
lastName: string;
phoneNumber: string;
role: string;
companyName: string;
industry: string;
}
Observability · SDK
function handleLogin(user: User) {
// BAD: full user object lands in logs
datadogLogger.info("User logged in", { user });
// GOOD: only operational metadata
const { deviceType, ipAddress, hostname } = getSystemInfo();
datadogLogger.info("User logged in", { deviceType, ipAddress, hostname });
}
Analytics · Web SDK
function trackUserSignup(user: User) {
// BAD: object spread leaks every field
gtag("event", "user_signup", { ...user });
// GOOD: only permitted fields
const { deviceType, browserUsed, ipAddress } = getDeviceInfo();
gtag("event", "user_signup", { deviceType, browserUsed, ipAddress });
}
CRM · REST API
function syncUserToSalesforce(user: User) {
// BAD: spreads the SSN and internal IDs into Salesforce
sendToSalesforce("lead_create", { ...user });
// GOOD: explicit, expected CRM fields only
sendToSalesforce("lead_create", {
firstName: user.firstName, lastName: user.lastName,
email: user.email, phoneNumber: user.phoneNumber,
companyName: user.companyName, role: user.role, industry: user.industry });
}
LLM API · Tainted prompt
let promptContext = {
audience: "Customer",
notes: "Welcome to our platform.",
};
// BAD: the variable becomes tainted with PII
promptContext.audience = `${user.firstName} ${user.lastName}`;
promptContext.notes = `Welcome ${user.email} to the ${user.industry} platform.`;
// GOOD: use only non-identifying metadata in the prompt
const prompt = `Generate a welcome message for a ${user.role} in the ${user.industry} sector.`;
| Scenario | Platform | Exposed (sensitive fields sent) | Safe (expected fields) |
|---|---|---|---|
| Full user object to Datadog | Datadog | email, ssn, firstName, lastName, phoneNumber, role, companyName, industry | hostname, ipAddress, deviceType |
| Tainted variables in OpenAI prompt | OpenAI | email, firstName, lastName | role, industry, companySize, age, gender |
| Full user object to Google Analytics | Google Analytics | email, ssn, firstName, lastName, phoneNumber, role, companyName, industry | ipAddress, deviceType, browserUsed |
| Full user object to Salesforce | Salesforce | ssn | firstName, lastName, email, phoneNumber, role, companyName, industry |
Asking questions in plain English
With the self-hosted or cloud platform, your organization’s data map becomes queryable in plain English.
An AppSec engineer asks which sensitive data and auth tokens are leaking into application logs.
Show me all sensitive data and auth tokens leaking in application logs
New chat
Show me all sensitive data and auth tokens leaking in application logs
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
A privacy engineer asks which third-party integrations receive PII.
Which third parties receive PII?
New chat
Which third parties receive PII?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
An AI governance team asks which AI integrations exist and what sensitive data reaches them.
Which AI services receive sensitive data in our code?
New chat
Which AI services receive sensitive data in our code?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
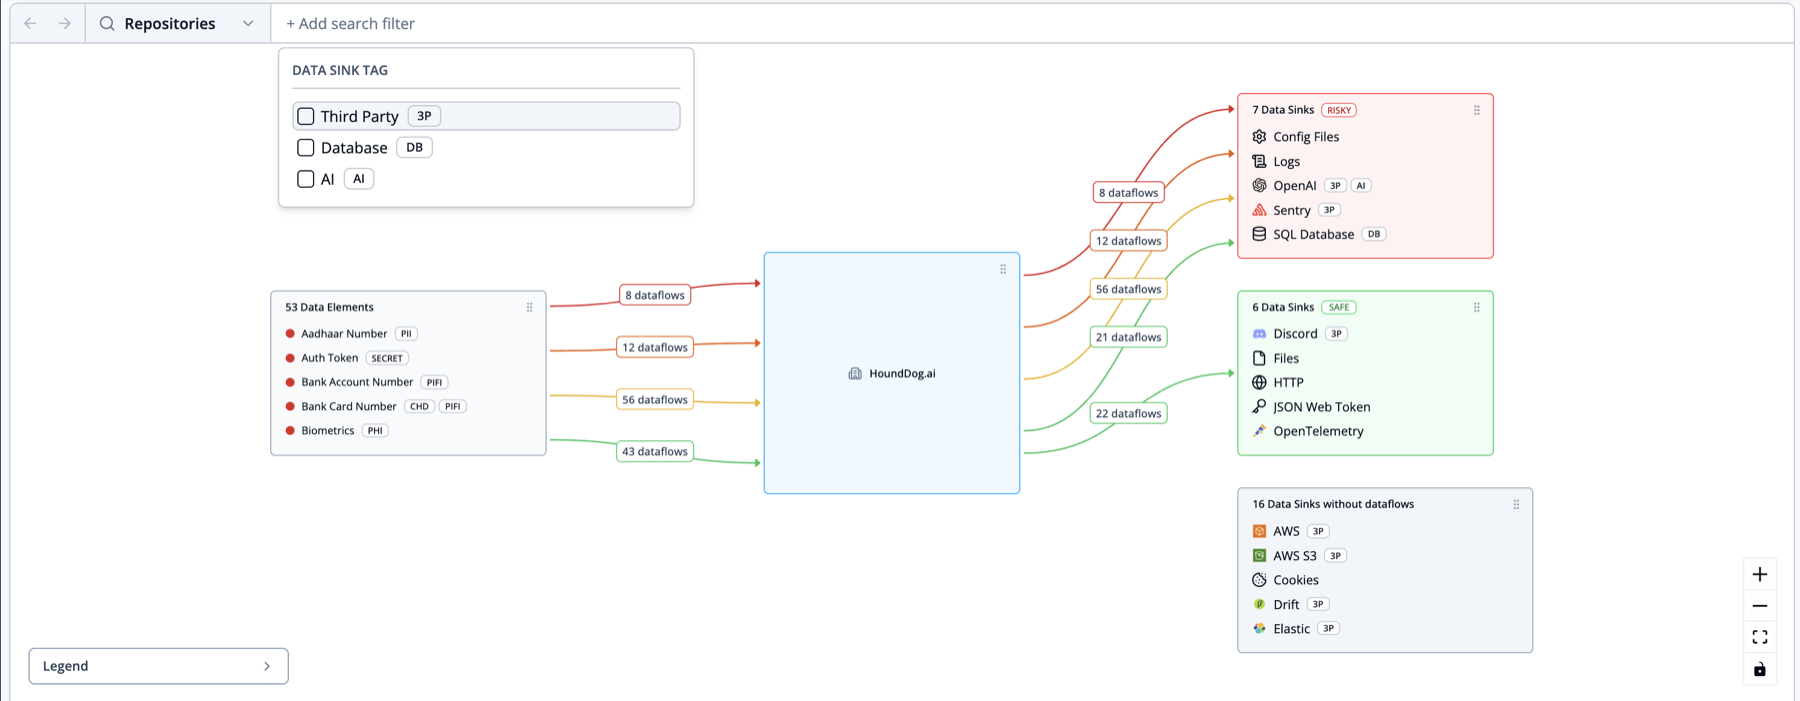
main branch of the hounddogai/hounddog-test-python repository, in one file.Dataflows: one confirmed dataflow, and it is risky.
Without AI, the Datamap is still available, built from the scanner’s deterministic findings. You can apply the same advanced filters to search for dataflows; there is no chat panel and no AI review.
Read the Datamap docs Related: DPA EnforcementAI GovernanceData Flow MappingPrivacy Code Scanning
Static analysis discovers. AI reasons. MCP delivers.
HoundDog.ai is built to make your AI more effective, not to replace it.
The scanner discovers every sensitive dataflow, so your AI tokens go to reasoning over detected flows: assessing risk, triaging dataflows and answering questions about your datamap.
The same commit always produces the same dataflows. Every engineer, privacy reviewer and agent gets the same answer about where sensitive data goes, instead of output that varies with the prompt.
The Rust scanner runs in CI on standard CPU infrastructure, across every repo and every commit, with negligible impact on build times.
Methods compared
Network, gateway, and storage-layer tools have a role, but they are reactive: they sanitize or alert after data has been collected. Only code-layer monitoring catches unsafe flows before deployment, while remediation is cheap and the engineer who made the change still has the context to fix it.
| Method | Layer | Pros | Cons |
|---|---|---|---|
| Static code analysis HoundDog.ai | Code | Continuous, pre-deployment detection, scales across repos, works on developer and AI-generated code, integrates with PR workflow | May miss data generated only at runtime |
| Manual code reviews | Code | Human judgment, can catch complex context-based issues | Time-consuming, not scalable, prone to human error |
| API gateway monitoring | API | Centralized control over API traffic, can log, redact, or block | Requires all traffic to pass through the gateway, misses traffic that bypasses it such as SDKs and internal services |
| Network proxy | Network | No need to modify application code | Hard to scale across microservices, lacks understanding of data context or meaning |
| Data Loss Prevention (DLP) | Network / Storage | Detects sensitive data in transit or at rest, integrates with the broader security stack | Reactive rather than preventative, lacks visibility into app-layer data flows and third-party SDKs |
Hardcoded regex rules for DIY detection are brittle, hard to maintain, and almost never scale. They lack context around data sensitivity, awareness of sanitization or transformations, and visibility into where data actually ends up. As codebases evolve, DIY coverage falls behind. HoundDog.ai's static analysis is purpose-built to do this at scale.
Why current approaches fall short
Posture and enforcement tools only act once sensitive data is already there. Catching the exposure at the source is the missing layer.
Questions
Third-party data flow monitoring is continuous, code-level visibility into which sensitive data elements your application sends to which third-party SDKs, APIs, and AI integrations. Unlike point-in-time audits, monitoring runs on every commit and pull request, so the data map stays accurate as the codebase evolves and new integrations are introduced.
DLP, DSPM, and CSPM operate after data is already at rest or in transit. They detect leaks once sensitive data has reached logs, storage, or a third party. HoundDog.ai operates at the code layer before the data starts flowing, so unsafe data exposures are stopped at the source rather than scrubbed reactively.
HoundDog.ai parses your source code to identify every third-party SDK, API call, and AI client embedded in the application, including ones added by developers or AI coding assistants without privacy or security review. New integrations show up as suggested updates the moment they appear in a pull request.
Yes. AI SDKs and LLM endpoints are first-class third-party sinks. HoundDog.ai traces tainted variables flowing into prompt templates and LLM calls, so PII or PHI that ends up inside an OpenAI, Anthropic, or LangChain prompt is monitored the same way as data written to an analytics SDK or CRM API.
Monitoring is the visibility layer. DPA enforcement is the gating layer that blocks pull requests that send data outside the per-vendor allowlist. Most teams turn on monitoring first to understand current state, then add enforcement on the integrations where a Data Processing Agreement defines a precise boundary.
See it in action
A short walkthrough of how HoundDog.ai discovers third-party integrations, traces sensitive data flows to each one, and surfaces unsafe flows in the pull request before they ship.
Try the free Privacy Code Scanner and see exactly which sensitive data elements reach each SDK, API, and AI integration in your codebase.