Introduction
Is your development team logging more data than necessary? Developers often log excessive data to keep applications running smoothly, even though this can clash with security practices. This article explores the reasons behind detailed logging, the security risks it creates, how to balance functionality and safety, and how to catch PII exposure in logs before it ever reaches production.
Understanding the Developer vs. Security Professional Psyche
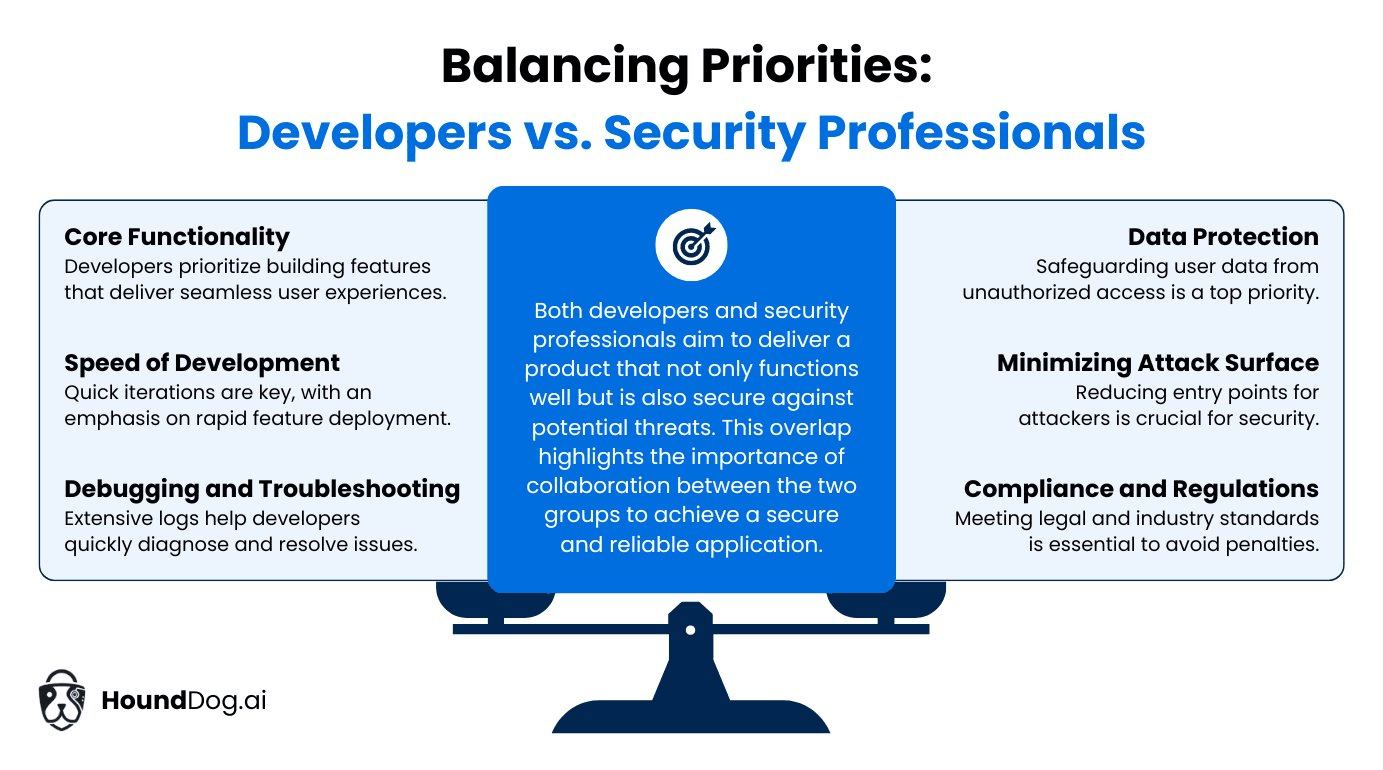
Developers want their apps to run smoothly and meet user needs. They use logs, a detailed diary of what the app does, to see what is happening under the hood and fix issues.
Security professionals, on the other hand, are all about keeping the app safe from threats. They go through everything with a fine tooth comb, especially the logs, to ensure nothing sensitive gets out.
There is a natural tug of war between the two. Developers log lots of detail to keep the app humming and troubleshooting fast, sometimes including sensitive information; security teams want logs brief and see every one of those entries as a potential leak. Overlogging is where these priorities collide. Balancing deep insight with strong protection is an ongoing challenge, and it is key to shipping safe, effective software.
Why Developers Overlog
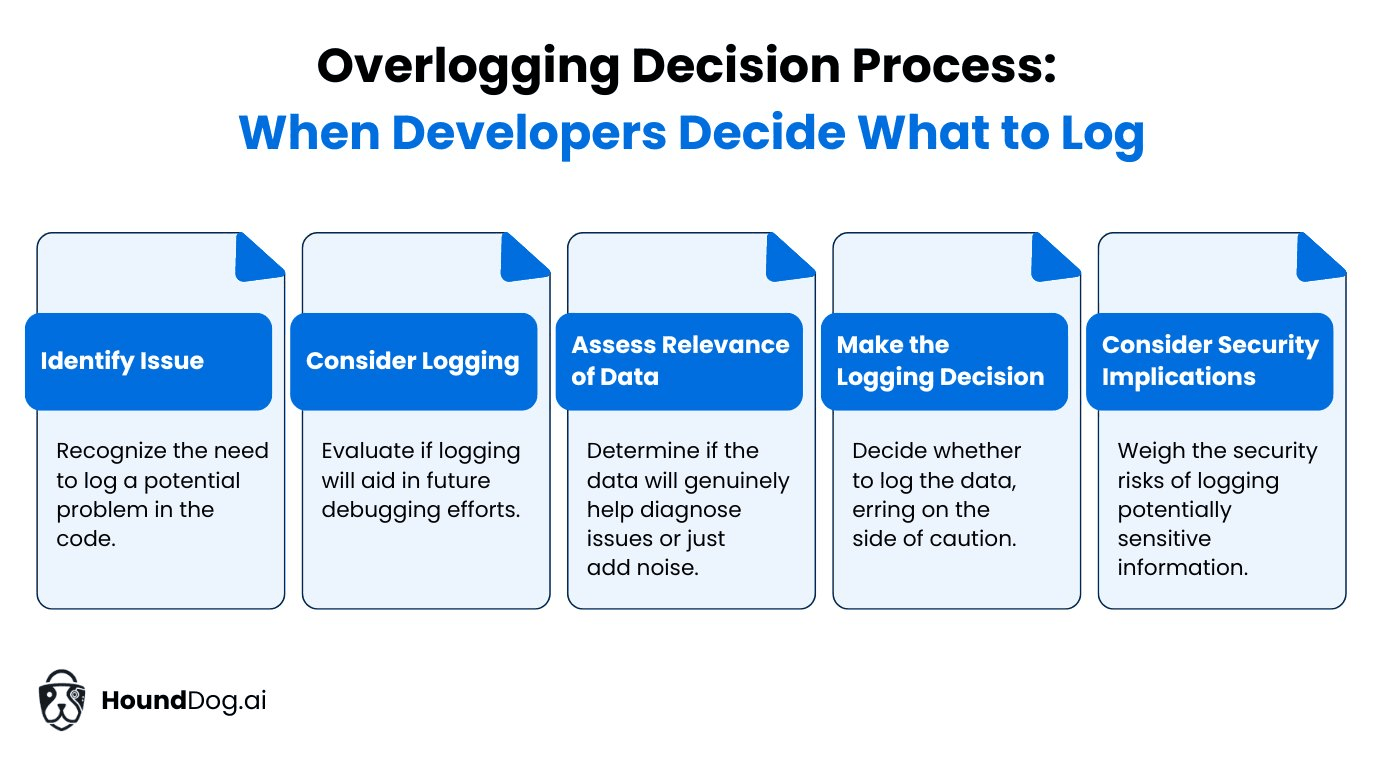
Developers often overlog to find the root cause of issues faster. When something goes wrong, detailed logs pinpoint where the problem started, which is especially valuable in complex systems where errors are subtle or masked by other processes.
Sometimes the logging is habit or precaution: the fear of missing a crucial detail during a future incident leads to logging everything just in case. Much of that data is never used, but to the person writing the code, the peace of mind is often worth it. The problem is what rides along: full request objects, user records, tokens, and identifiers that were never meant to live in a log file.
The Security Risks of Overlogging
An expanded attack surface
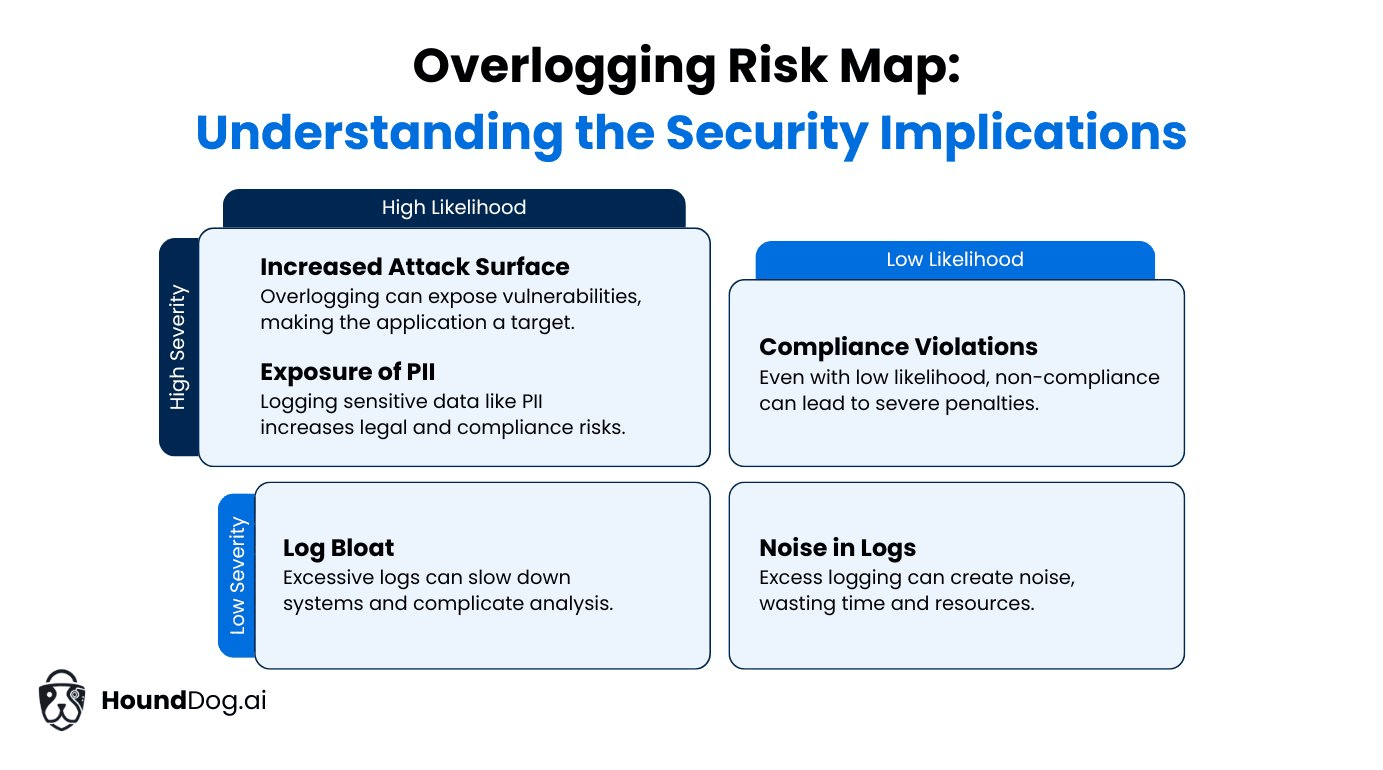
Logging too much inadvertently increases the application's attack surface: each piece of logged data, especially if not properly protected, becomes a potential entry point. Logs without secure management and restricted access can be read or intercepted, particularly when stored without sufficient controls or transmitted over unsecured channels.
CWE-532, CWE-210, and OWASP ASVS
The OWASP Application Security Verification Standard (ASVS) and the Common Weakness Enumeration catalog the vulnerabilities that arise from improper log handling. CWE-532 (insertion of sensitive information into a log file) and CWE-210 focus directly on the patterns behind PII exposure in logs. Logging sensitive data without proper controls breaches privacy norms and violates compliance regulations.
The trap of non mission critical apps
Non mission critical applications often carry less stringent security measures, making them prime targets if they log sensitive information, because developers assume they will not attract attackers and give their logging less scrutiny. But any application that logs PII must enforce strict controls, regardless of how unimportant the app seems. The real world impact is severe: numerous incidents of excessive PII logging have led to significant breaches, compliance violations, and financial penalties, and once customer trust is broken, rebuilding it is far harder than preventing the leak would have been.
Why Remediating PII in Logs Is So Hard
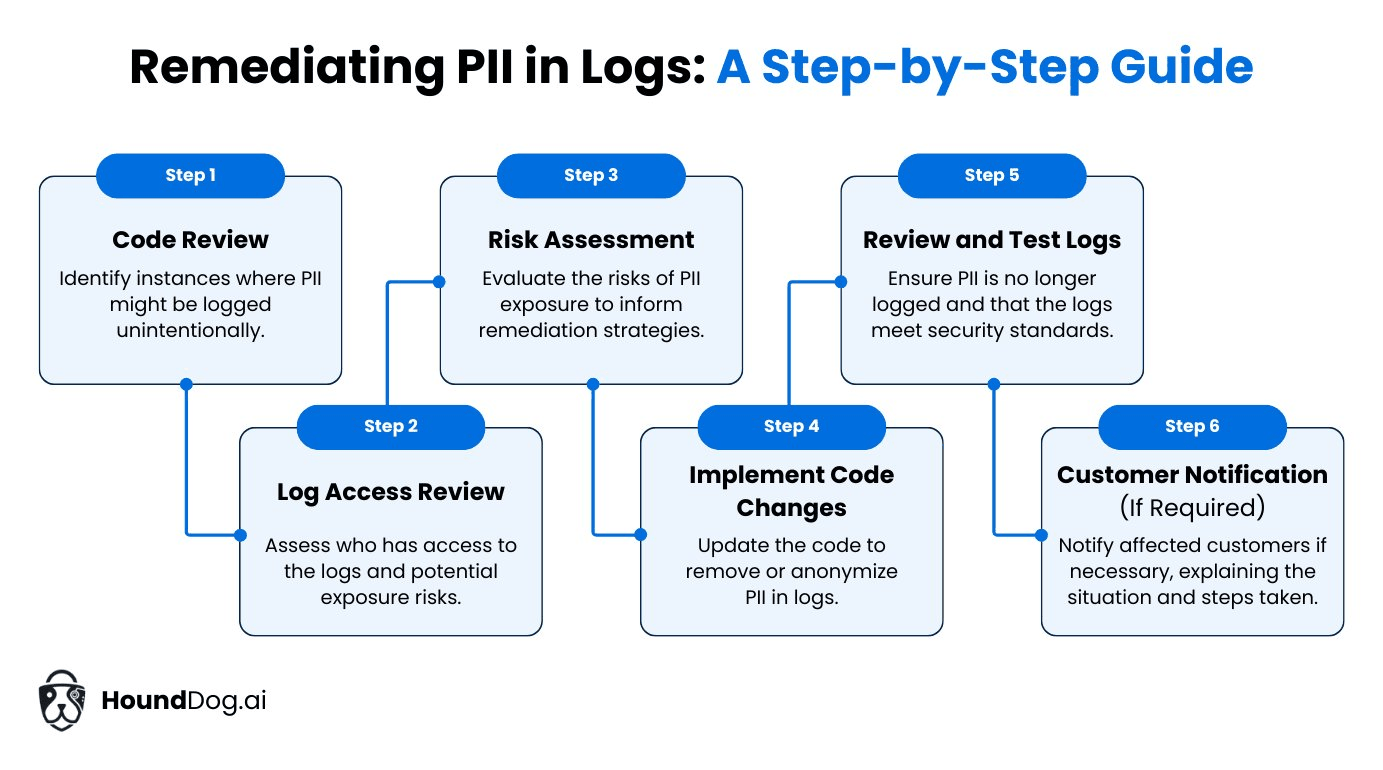
Addressing PII in logs is no small task. It involves updating code so the data stops being logged, sifting through existing logs to identify and purge what already leaked, and running risk assessments to understand the exposure and prevent recurrence. Each step takes significant time and expertise, and requires knowing what counts as sensitive under each applicable compliance framework.
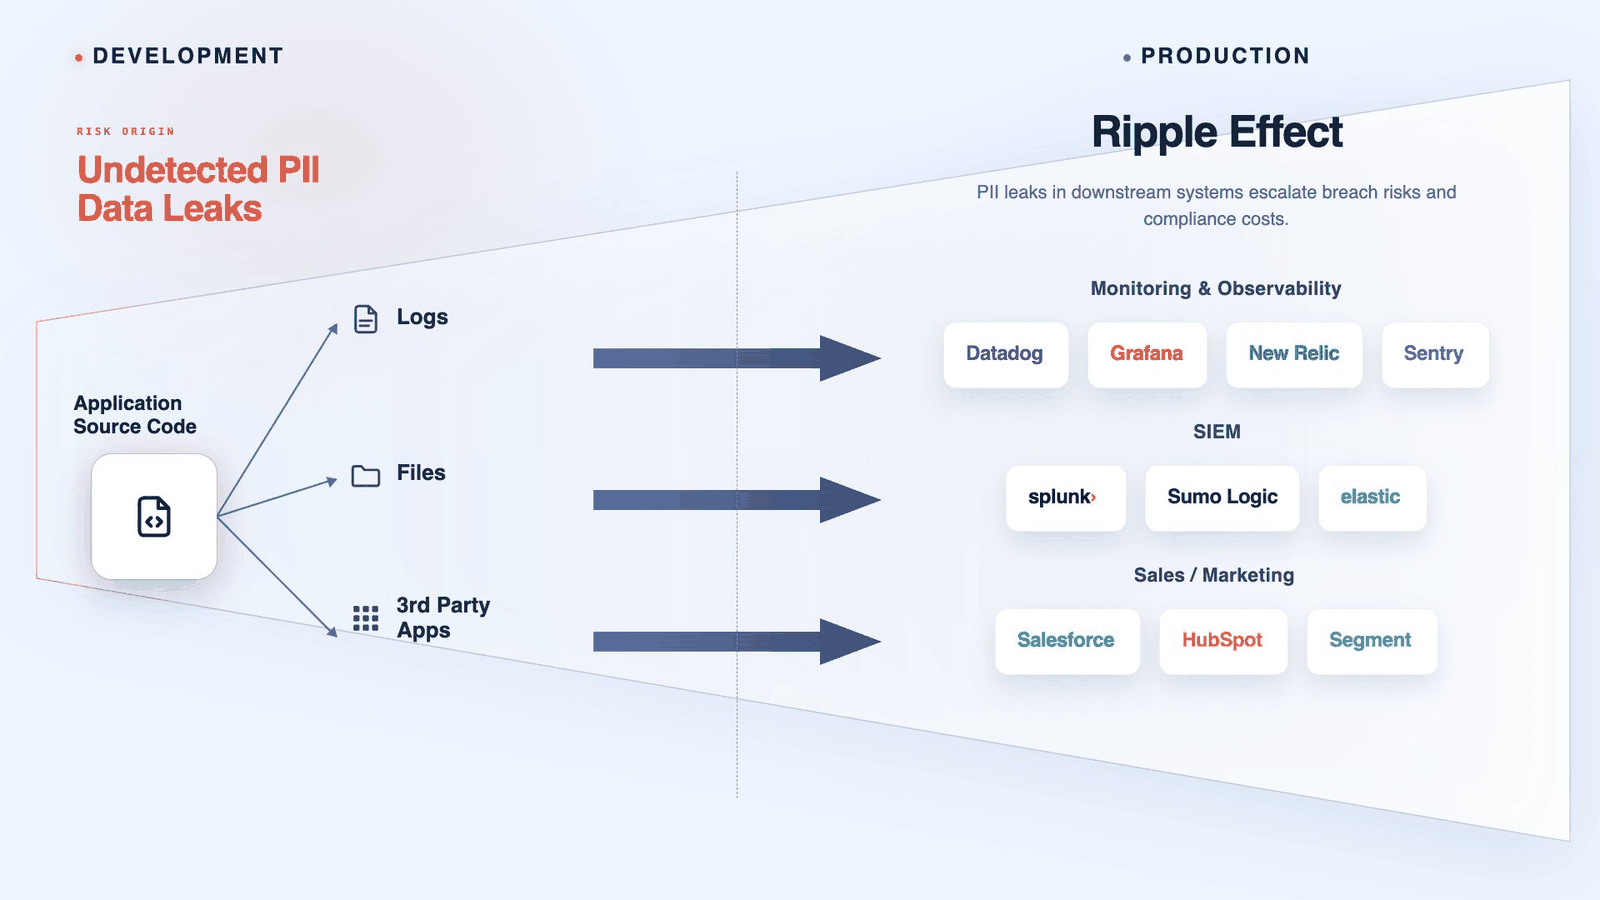
The hardest part is that leaked PII does not stay in one place. Logs are ingested by every downstream system attached to them: monitoring and observability platforms, SIEM tools, backups, and analytics pipelines. One leaked field suddenly lives in a dozen third party systems, each with its own data handling protocols, and security teams are left playing whack a mole across all of them.
Legal and Reputational Risks: Notifications and Compliance
When PII is mishandled, the fallout extends beyond the technical realm. Companies face legal repercussions for failing to comply with data protection laws like GDPR or HIPAA, including significant fines and mandatory corrective actions. If a breach compromises customer data, notifying affected individuals is not just a legal requirement; it is a critical moment in managing the company's reputation, and mishandling it further erodes trust.
Remediation is also resource heavy: dedicated staff to manage the cleanup, tooling to securely erase or modify sensitive data, and the opportunity cost of every hour spent identifying, rectifying, and preventing PII exposure after the fact instead of on other development and security priorities.
The Need for Proactive Sensitive Data Protection
Building security into the code from the beginning changes the economics entirely. When developers consider data handling as they write, sensitive information stays protected throughout the application's life: encryption in transit and at rest, sound coding practices, and clear rules about what data is allowed to land where.
Shift left to prevent PII leaks and overlogging
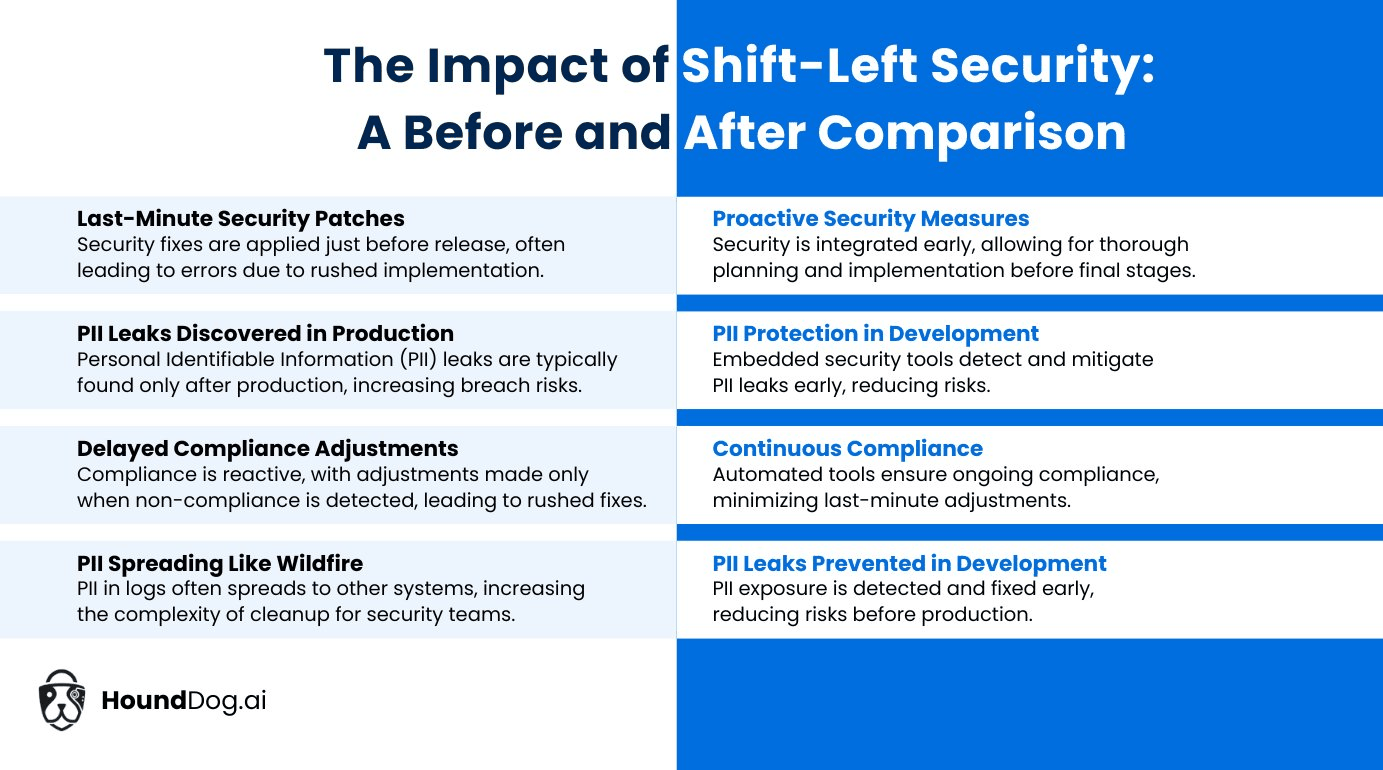
Catching problems early, when they are cheaper and easier to fix, is the core argument for shift left data leak prevention. The earlier logging discipline is enforced, the lower the chance that unnecessary or risky data gets logged at all, and the smaller the cleanup that ever needs to happen.
How HoundDog.ai helps
The HoundDog.ai Privacy Code Scanner catches overlogging before it ships. Repository scans cover the existing codebase, and CI/CD checks flag PII flowing into logs before merge. The scanner traces sensitive data interprocedurally, so it catches the indirect cases too: the full user object passed to a logger three calls away from where the data entered.
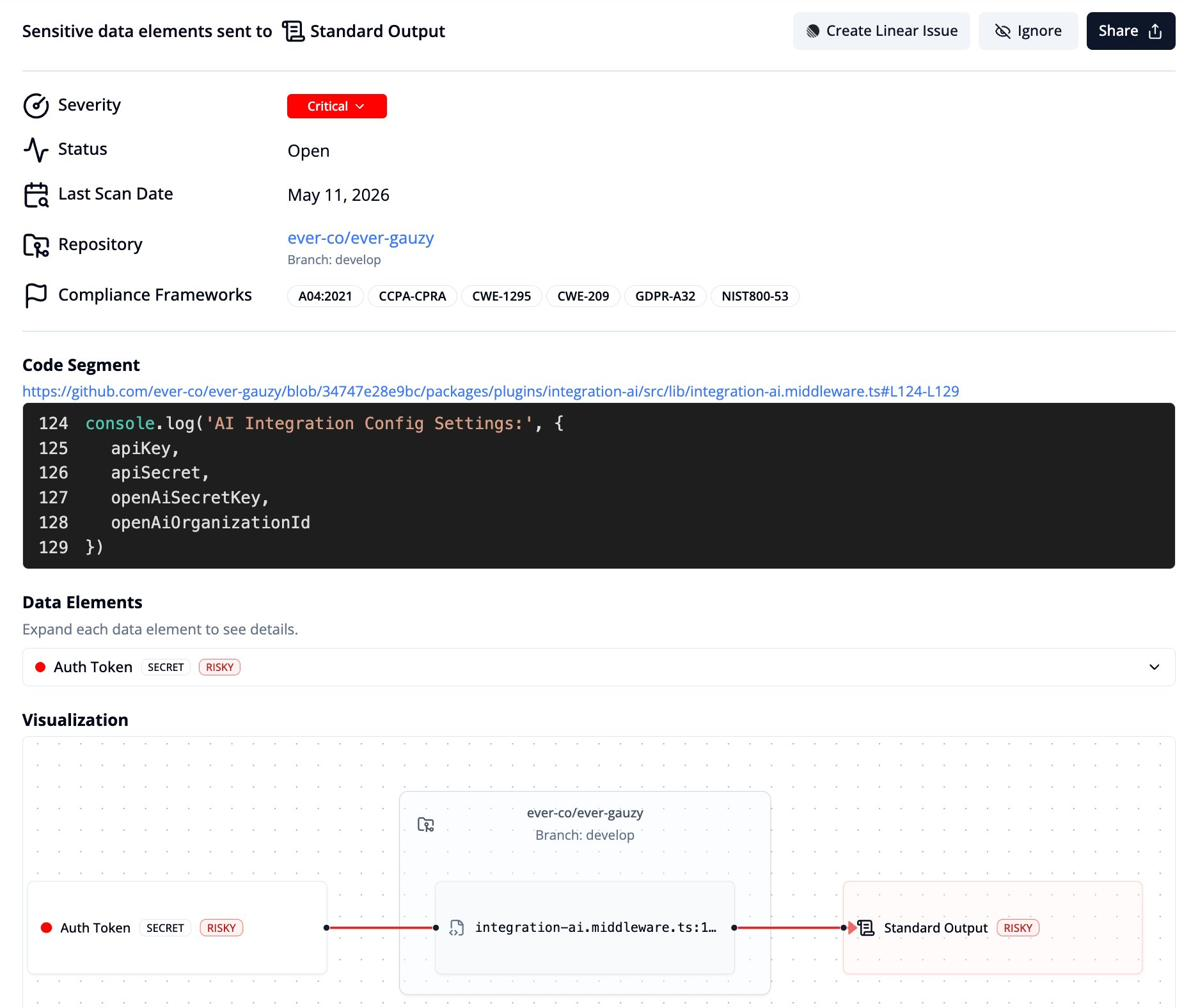
Automated compliance checks in the pipeline keep data handling aligned with privacy requirements without slowing development, and automated enforcement makes building secure apps far less error prone.
Conclusion
We covered why developers log so much data, the security risks and legal exposure this creates, especially around PII, and why cleanup after the fact is so painful. Logs are essential for troubleshooting and performance, but they have to be secured, and the cheapest place to secure them is in the code, before anything ships. Book a demo with HoundDog.ai to see how proactive PII leak detection keeps sensitive data out of your logs entirely.