Privacy Code Scanner · Regulation (EU) 2024/1689
Build an accurate AI inventory directly from source code, trace personal and sensitive data flowing into LLM prompts and AI APIs, and produce the Article 11 technical documentation EU AI Act compliance expects. Code-based evidence, before anything reaches production.
The Stakes
The regulation is in force, with prohibitions and General-Purpose AI rules already enforceable. The Digital Omnibus agreement of 7 May 2026 deferred the headline high-risk deadlines, but several obligations apply immediately and the work to meet them takes time.
€35M / 7%
Of global annual turnover, whichever is higher, for prohibited AI practices. Higher than GDPR's 4 percent ceiling.
Aug 2026 · Dec 2027
Article 50 transparency obligations apply from 2 August 2026. Annex III high-risk obligations deferred to 2 December 2027 under the Digital Omnibus.
50%+
Industry readiness analysis through 2026. Without a systematic inventory, risk classification and Article 11 documentation are not possible.
Where Teams Get Stuck
Compliance leaders know which Articles apply. The harder question is how to prove the application behaves the way the documentation says it does.
Engineering ships OpenAI, Anthropic, Gemini, and agent-framework integrations through pull requests. None of these reach procurement.
AI Act Art. 6 · Art. 11PII exposures to AI integrations are rarely intentional. They happen as codebases grow.
AI Act Art. 10 · GDPR Art. 9Agile teams ship every week. Technical documentation written at design time is stale before the next sprint.
AI Act Art. 11 · Annex IVPersonal data entering an AI system is governed by both regimes. Two regulators, two penalty schedules, one root cause.
GDPR Art. 32 / 35 · AI Act Art. 10The Regulation
The AI Act is risk-based. Obligations escalate with the potential harm a system could cause. The four tiers determine what your team has to produce and which deadline applies to you.
Spam filters, recommendation engines, inventory optimization, and most general AI use. Providers are encouraged to adopt voluntary codes of conduct. No specific obligations.
Chatbots, generative AI, emotion-recognition systems, and biometric categorization. Users must be told they are interacting with AI. AI-generated content must be machine-readable as synthetic. Applies from 2 August 2026.
Annex III systems in recruitment, credit scoring, education, employment, law enforcement, migration, and justice. Plus Annex I product-embedded AI in regulated products. Risk management, data governance, technical documentation, logging, human oversight, and registration in the EU database.
Social scoring, subliminal manipulation, untargeted facial scraping, emotion recognition in workplaces and schools, real-time biometric identification in public spaces. New for December 2026: AI-generated CSAM and non-consensual intimate imagery.
For Privacy Teams
At development speed. Build your AI inventory and Article 11 technical documentation from source code, with privacy teams in control: the engine proposes, the DPO approves.
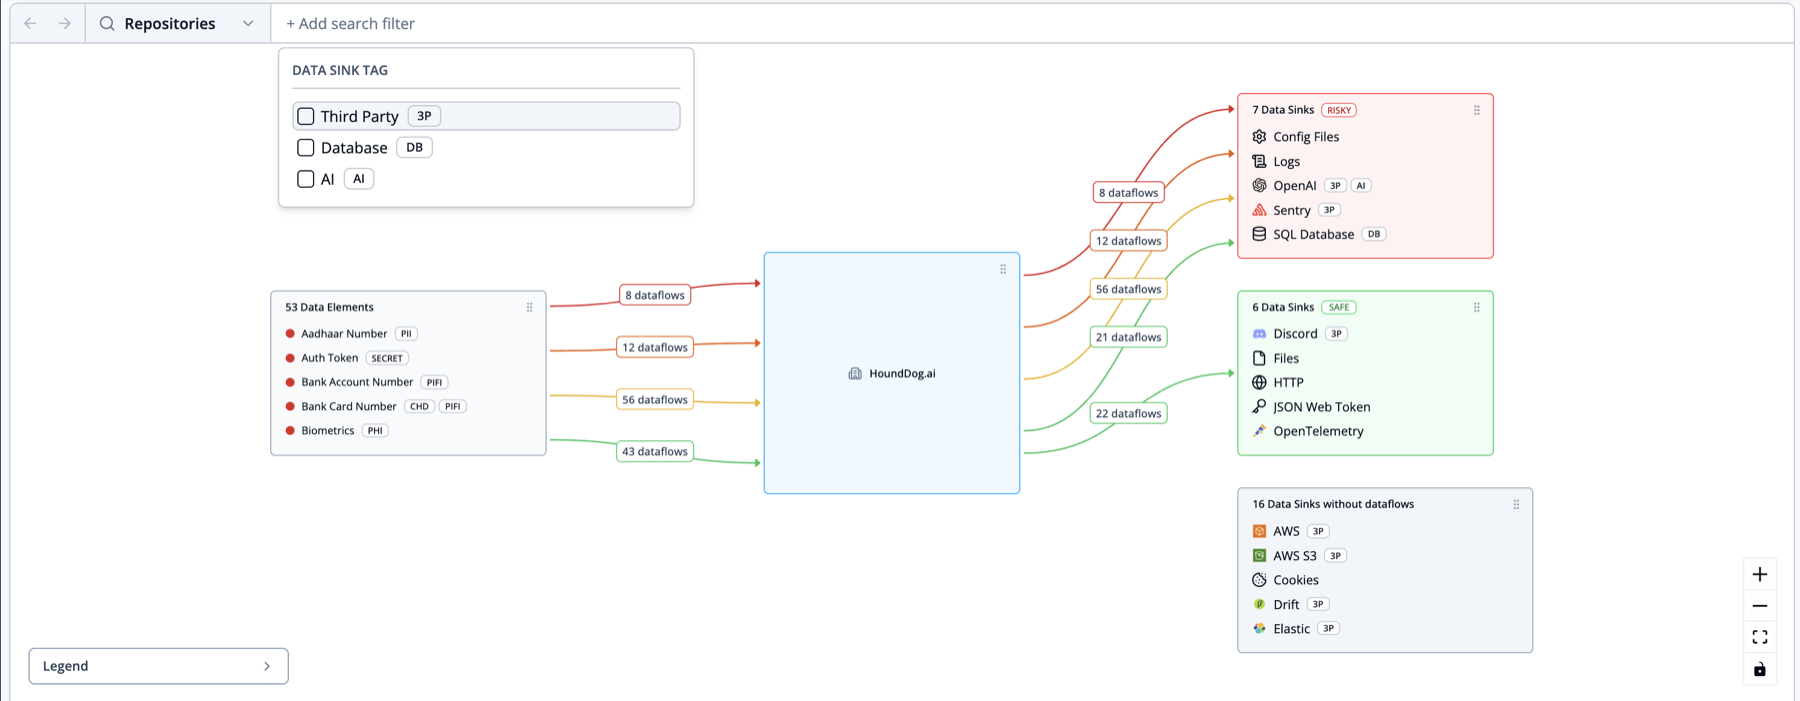
All third-party and AI integrations detected directly in source code, including Shadow AI, whether the data flows through an SDK or API, with 1,000+ integrations covered out of the box.
Trace 100+ sensitive data types (PII, PHI, CHD, auth tokens) across code paths into logs, storage, APIs, and third-party and AI integrations.
Keep your RoPA updated as new categories of personal data and subprocessors are introduced, detected directly from source code.
Validate design-phase privacy reviews with code-based evidence before code is pushed to production.
Suggest
Org RoPA updates
Verify
Alignment with PIA
Block
Risky data flows
Catch
Log leaks early
Article Mapping
A side-by-side view of where the regulation makes specific requirements and the code-based evidence HoundDog.ai surfaces for each. Designed to be shared with auditors and DPOs.
| Requirement | What it asks for | Code-based evidence from HoundDog.ai |
|---|---|---|
| AI inventoryArt. 6, foundational | Identify which AI systems the application uses so risk tier can be assigned. | Static analysis enumerates every AI integration in source code, including SDK-based and indirect agent-framework usage, with file and call-site provenance. |
| Data governanceAI Act Art. 10 | Document categories of personal and sensitive data processed by AI systems. | Taint-flow analysis traces 100+ data types into each AI sink, each tagged PII, PHI, PIFI, CHD, or SECRET, with a sensitivity level. |
| Risk managementAI Act Art. 9 | Identify, evaluate, and mitigate risks throughout the system lifecycle. | Risky data flows are surfaced at PR time with severity rating, providing a continuous risk register tied to code changes rather than periodic reviews. |
| Technical documentationAI Act Art. 11, Annex IV | Maintain records of design, data, validation, and monitoring sufficient for authority review. | Every scan produces reproducible evidence of which AI systems are called, what data they receive, and from where, exportable as audit-ready artifacts. |
| Record-keepingAI Act Art. 12 | Automatic logging of events relevant to risk identification and post-market monitoring. | Code-level provenance for every detected flow: repository, file, line, function. Persistent and queryable across scans, with diffs between runs. |
| TransparencyAI Act Art. 50, from Aug 2026 | Disclose AI interactions to users. Mark AI-generated content as synthetic. | An inventory of the AI integrations detected, and the data each receives, helps determine which Article 50 disclosures apply per feature. |
| Privacy by designGDPR Art. 25 | Build minimization, access controls, and protection into the architecture from the start. | CI integration blocks unapproved AI data sharing in pull requests, shifting privacy enforcement to design and development phases. |
| DPIAGDPR Art. 35 | Assess and document high-risk processing before it begins. | Auto-generate Data Protection Impact Assessments pre-populated with detected data flows, AI integrations, and identified risks. |
| Records of ProcessingGDPR Art. 30 | Maintain a register of processing activities and subprocessors. | New AI integrations and subprocessors appear as suggested RoPA edits for privacy team review and approval, traceable to the code change. |
Dual Regime Reality
The AI Act does not replace GDPR. Personal data flowing into AI systems is still governed by GDPR, with full penalties. The two regimes overlap at every layer of an AI feature, so the safest assumption is that both apply.
| Topic | What this means for LLM use | Primary legal basis | Maximum penalties |
|---|---|---|---|
| Lawful basis | A valid lawful basis must be selected before any personal data is processed by the model or provider. | GDPR Art. 6 | Up to 20M EUR or 4% of global revenue |
| Special categories | Special categories cannot be processed unless an Article 9 exception applies with strong safeguards. | GDPR Art. 9 | Higher tier penalties |
| Privacy by design | Controls for minimization, access, and protection must be built into the architecture from the start. | GDPR Art. 25 | Higher tier penalties |
| Security of processing | Encryption, logging, and strong access controls must be in place across AI data paths. | GDPR Art. 32 | Penalties scale with severity |
| Transparency and user rights | Users must be informed and allowed access, correction, deletion, and objection over their data. | GDPR Art. 12-15, 21 | Penalties vary |
| International transfers | Valid transfer mechanisms and documented assessments are required when AI providers operate outside the EU. | GDPR Art. 44-49 | Penalties vary |
| Prohibited AI practices | Social scoring, manipulation, untargeted biometric scraping, and emotion recognition at work or school are banned. | AI Act Art. 5 | Up to 35M EUR or 7% of global turnover |
Asking questions in plain English
With the self-hosted or cloud platform, your organization’s data map becomes queryable in plain English.
An AppSec engineer asks which sensitive data and auth tokens are leaking into application logs.
Show me all sensitive data and auth tokens leaking in application logs
New chat
Show me all sensitive data and auth tokens leaking in application logs
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
A privacy engineer asks which third-party integrations receive PII.
Which third parties receive PII?
New chat
Which third parties receive PII?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
An AI governance team asks which AI integrations exist and what sensitive data reaches them.
Which AI services receive sensitive data in our code?
New chat
Which AI services receive sensitive data in our code?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
main branch of the hounddogai/hounddog-test-python repository, in one file.Dataflows: one confirmed dataflow, and it is risky.
Without AI, the Datamap is still available, built from the scanner’s deterministic findings. You can apply the same advanced filters to search for dataflows; there is no chat panel and no AI review.
Read the Datamap docs Related: AI GovernanceRoPAPrivacy Impact AssessmentPrivacy Code Scanning
Static analysis discovers. AI reasons. MCP delivers.
HoundDog.ai is built to make your AI more effective, not to replace it.
The scanner discovers every sensitive dataflow, so your AI tokens go to reasoning over detected flows: assessing risk, triaging dataflows and answering questions about your datamap.
The same commit always produces the same dataflows. Every engineer, privacy reviewer and agent gets the same answer about where sensitive data goes, instead of output that varies with the prompt.
The Rust scanner runs in CI on standard CPU infrastructure, across every repo and every commit, with negligible impact on build times.
FAQ
The Articles, deadlines, and roles teams ask about most when scoping their AI Act program.
Yes, if the AI system is placed on the EU market or its outputs affect people in the EU. The EU AI Act has extraterritorial reach similar to GDPR. A US or UK company whose AI features are used by EU customers is in scope, regardless of where the model runs.
The Digital Omnibus provisional agreement of 7 May 2026 deferred the headline compliance dates. Annex III high-risk AI obligations move from 2 August 2026 to 2 December 2027. Annex I product-embedded high-risk systems move from 2 August 2027 to 2 August 2028. Article 50(2) watermarking moves to 2 December 2026. Prohibited practices under Article 5 and General-Purpose AI obligations remain in force unchanged, and the August 2026 transparency obligations under Article 50 still apply.
Most teams that wrap a foundation model in a product feature are deployers under the AI Act. Substantial fine-tuning, retraining, or rebranding can reclassify you as a provider, which carries heavier documentation and conformity obligations. The boundary is interpretive, so map your AI usage carefully and document the modifications your engineering team makes.
HoundDog.ai produces code-based evidence of which AI systems your application calls, which categories of personal and sensitive data flow into each one, and which file, function, and call site each integration originates from. This evidence is reproducible across every scan, traceable to the code that generated it, and is exactly the documentation Article 11 expects organizations to maintain.
Violations of Article 5 prohibited AI practices carry the highest tier, up to 35 million euros or 7 percent of global annual turnover, whichever is higher. Non-compliance with other obligations such as data governance, technical documentation, and transparency carries fines up to 15 million euros or 3 percent of global turnover. Supplying incorrect information to authorities carries up to 7.5 million euros or 1 percent.
No. HoundDog.ai runs in your development environment or CI pipeline and analyzes source code statically. It never needs access to your production database, runtime data, live AI traffic, or model providers. All evidence is generated before code reaches production.
Build an accurate AI inventory, trace personal data into every LLM prompt, and produce the Article 11 technical documentation your auditors will ask for. From source code, before anything ships.