Records of Processing Activities (RoPA)

Keep your GDPR Article 30 RoPA continuously updated with suggested edits surfaced directly from code scans. Privacy teams stay in control of the review cycle.

Suggested RoPA Edits, Backed by Code Evidence

The hardest part of Article 30 compliance is not creating the document but keeping it accurate as applications evolve. HoundDog.ai closes that gap with a detect, suggest, approve workflow.

Detect

New data flows and AI or third-party subprocessors, scanned directly from source code on every CI run.

Suggest

RoPA edits proposed with code-level evidence. New subprocessors and personal data categories surface as structured suggestions.

Approve

The DPO reviews, approves, or rejects each suggestion. Nothing enters the Org RoPA without explicit privacy team sign-off.

HoundDog.ai Acme Corp
8 dataflows 12 dataflows 56 dataflows 43 dataflows 8 dataflows 12 dataflows 56 dataflows 21 dataflows 22 dataflows
53 Data Elements Aadhaar Number PII Auth Token SECRET Bank Account Number PIFI Bank Card Number CHDPIFI Biometrics PHI
HoundDog.ai
7 Data Sinks RISKY Config Files Logs OpenAI 3PAI Sentry 3P SQL Database DB
6 Data Sinks SAFE Discord 3P Files HTTP JSON Web Token OpenTelemetry
Sensitive data flows detected per data sink
Review of Acme Corp (Q2-2026) Waiting approval Approved Suggested by the scanner from the code · ropa.yml
Names of Subprocessors and DPA Status A list of all subprocessors along with the status of their Data Processing Agreement Stripe (DPA established)Adyen (DPA established)Sentry (DPA established)Datadog (DPA established)OpenAI (DPA established) Amplitude (DPA established) LangChain (DPA status unknown) Suggestion Stripe (DPA established)Adyen (DPA established)Sentry (DPA established)Datadog (DPA established)OpenAI (DPA established) Amplitude (DPA established) LangChain (DPA status unknown)
Review of TravelSoft (Q1-2026) Waiting approval Approved Suggested by the scanner from the code · ropa.yml
Categories of Personal Data The categories of personal data the processing covers Contact informationTravel and booking data Financial information Online identifiers Suggestion Contact informationTravel and booking data Financial information Online identifiers
Suggested edits queued for DPO review

What Are Records of Processing Activities (RoPA)?

Records of Processing Activities (RoPA) are required under Article 30 of the GDPR. They document how personal data is collected, used, shared, retained, and protected across an organization. A complete RoPA covers:

These obligations apply to controllers and processors alike, and to most organizations under 250 employees that process personal data regularly or handle special categories, which in practice covers most modern software companies. Supervisory authorities can request your RoPA at any time and expect it to reflect current operational reality, not a snapshot from last year's audit.

Why Processing Activities Fall Out of Sync with the Codebase

Privacy teams rely on three workflows today, and none of them keeps up with modern development.

Manual Documentation Does Not Scale

  • Engineering gets flooded with privacy questionnaires every release

Works at 10 apps. Breaks at 1,000.

GRC Platforms

  • Provide blank RoPA, PIA, and DPIA templates, like this one from Vanta, and leave privacy teams to interview engineers and collect data flows by hand

Ships the template, not the data flows.

Privacy Platforms Are Blind to the Codebase

  • Privacy platforms infer flows after deployment, missing shadow AI and SDKs added in code

Looks at production. Never at the code.

The result

Stale Evidence
Documentation runs months behind the code.
Drift
Documented activities drift from code each release.
Exposure
Undocumented subprocessors: an Article 30 risk.

Typical questions come from different teams

With the self-hosted or cloud platform, your organization’s data map becomes queryable in plain English.

A privacy engineer asks which third-party integrations receive PII.

Which third parties receive PII?

HoundDog.ai Acme Corp
New chat Which third parties receive PII? ···
Ask HoundDog.ai about your data Suggested for you Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
Which third parties receive PII?
Searching…
Searched the datamap
Opened a page
Two third-party data sinks receive PII, counting PHI, PIFI and CHD as PII. Both are in one repository, hounddogai/hounddog-test-python, on the main branch:
Third partyData elementTag and sensitivityDataflows
OpenAI Medical History PHI, high 1 risky dataflow
Sentry Phone Number PII, medium 1 risky dataflow
I've opened the Datamap's Data Sinks view filtered to these two sinks.
Datamap · Data Sinks
Which third parties receive PII? Ask about your data…
8 dataflows 12 dataflows 56 dataflows 43 dataflows 8 dataflows 12 dataflows 56 dataflows 21 dataflows 22 dataflows
53 Data Elements Aadhaar Number PII Auth Token SECRET Bank Account Number PIFI Bank Card Number CHDPIFI Biometrics PHI
HoundDog.ai
7 Data Sinks RISKY Config Files Logs OpenAI 3PAI Sentry 3P SQL Database DB
6 Data Sinks SAFE Discord 3P Files HTTP JSON Web Token OpenTelemetry
1 dataflow 1 dataflow 1 dataflow 1 dataflow
2 Data Elements Medical History PHI Phone Number PII
HoundDog.ai
OpenAI 3PAI RISKY
Sentry 3P RISKY
Without AI

The same Datamap, built from deterministic findings

Without AI, the Datamap is still available, built from the scanner’s deterministic findings. You can apply the same advanced filters to search for dataflows; there is no chat panel and no AI review.

  • By repository — select several, such as backend, frontend, and an authentication service, to see every dataflow across them.
  • By data element — “show me every repository where Social Security Number is processed” and every sink it may be exposed to.
  • By data sink — “show me all sensitive data sent to OpenAI org-wide.”
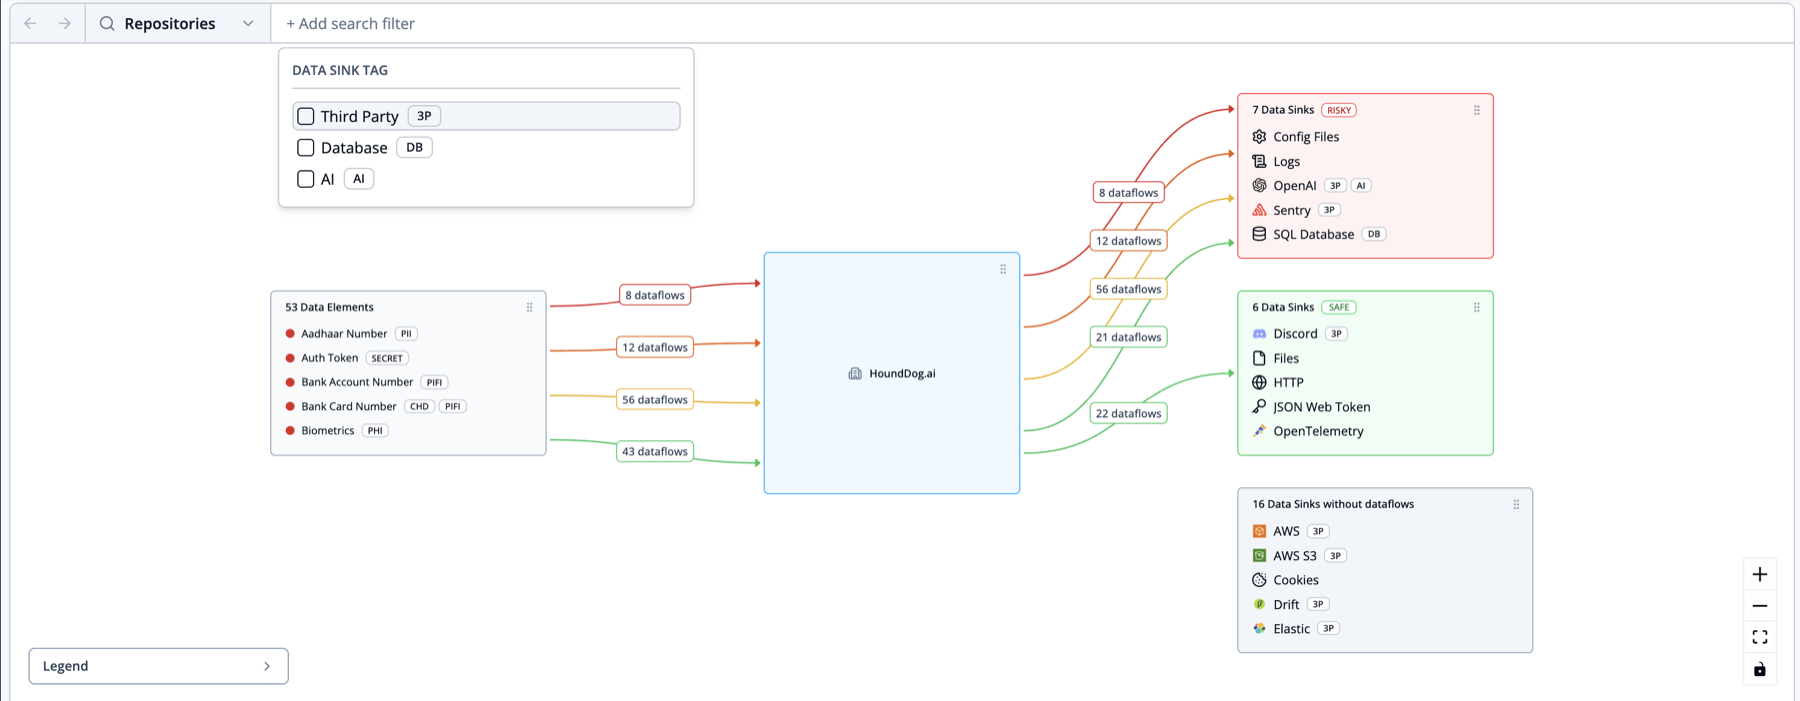
The Datamap without AI: 53 data elements flowing through HoundDog.ai into 7 risky data sinks, 6 safe data sinks, and 16 data sinks without dataflows, with the Data Sink Tag filter open

Why not just use an LLM?

HoundDog.ai is built to make your AI more effective, not to replace it.

01

Tokens for reasoning, not discovery.

The scanner discovers every sensitive dataflow, so your AI tokens go to reasoning over detected flows: assessing risk, triaging dataflows and answering questions about your datamap.

02

Evidence you can stand behind.

The same commit always produces the same dataflows. Every engineer, privacy reviewer and agent gets the same answer about where sensitive data goes, instead of output that varies with the prompt.

03

Easy to roll out org-wide.

The Rust scanner runs in CI on standard CPU infrastructure, across every repo and every commit, with negligible impact on build times.

Processing Purposes Based on What Applications Actually Do

Traditional RoPA tools document intended use. The HoundDog.ai Privacy Code Scanner documents actual use. That distinction matters when a regulator asks whether your records align with real system behavior, and it is the same code-level foundation that powers GDPR data mapping across your repositories.

Example: An application declares that email addresses are collected only for account creation. Code-level analysis reveals the same email field is also passed to a third-party analytics SDK and written to error logs. The accurate processing purposes are account management, analytics, and operational monitoring, and the RoPA suggestion reflects all three.

From Compliance Burden to Operational Asset

Built from code-level insight rather than periodic surveys, RoPA becomes a living system of record. Privacy, security, and engineering teams work from the same underlying data, and when supervisory authorities request records, the response is grounded in real application behavior. RoPA becomes part of privacy by design, built into how you ship rather than something you scramble to explain later.

RoPA Frequently Asked Questions

What is a RoPA under GDPR?

A Record of Processing Activities (RoPA) is the inventory of personal data processing required by Article 30 of the GDPR. It documents what personal data an organization processes, why, on what legal basis, who receives it, how long it is retained, and what security measures protect it.

Who is required to maintain records of processing activities?

Both data controllers and data processors must maintain RoPA. Organizations with fewer than 250 employees are also covered if they process personal data regularly, handle special categories of data, or carry out higher-risk processing, which in practice includes most software companies.

Can RoPA maintenance be automated?

Yes. HoundDog.ai automates the evidence-gathering half of RoPA maintenance: it scans source code, performs automated data mapping, and surfaces new data flows and subprocessors as suggested edits. The privacy team keeps full control of the review and approval cycle, so automation never bypasses human judgment.

Does HoundDog.ai send my source code anywhere?

No. Scans run inside your own CI pipeline, and your code never leaves your environment. Only scan findings, such as detected data flows and data sink metadata, are used to generate RoPA suggestions.

Make Privacy-by-Design a Reality in Your SDLC

Detect PII leaks, map sensitive data flows, and keep your Org RoPA current with code-based suggested edits.