Use case · Privacy & compliance
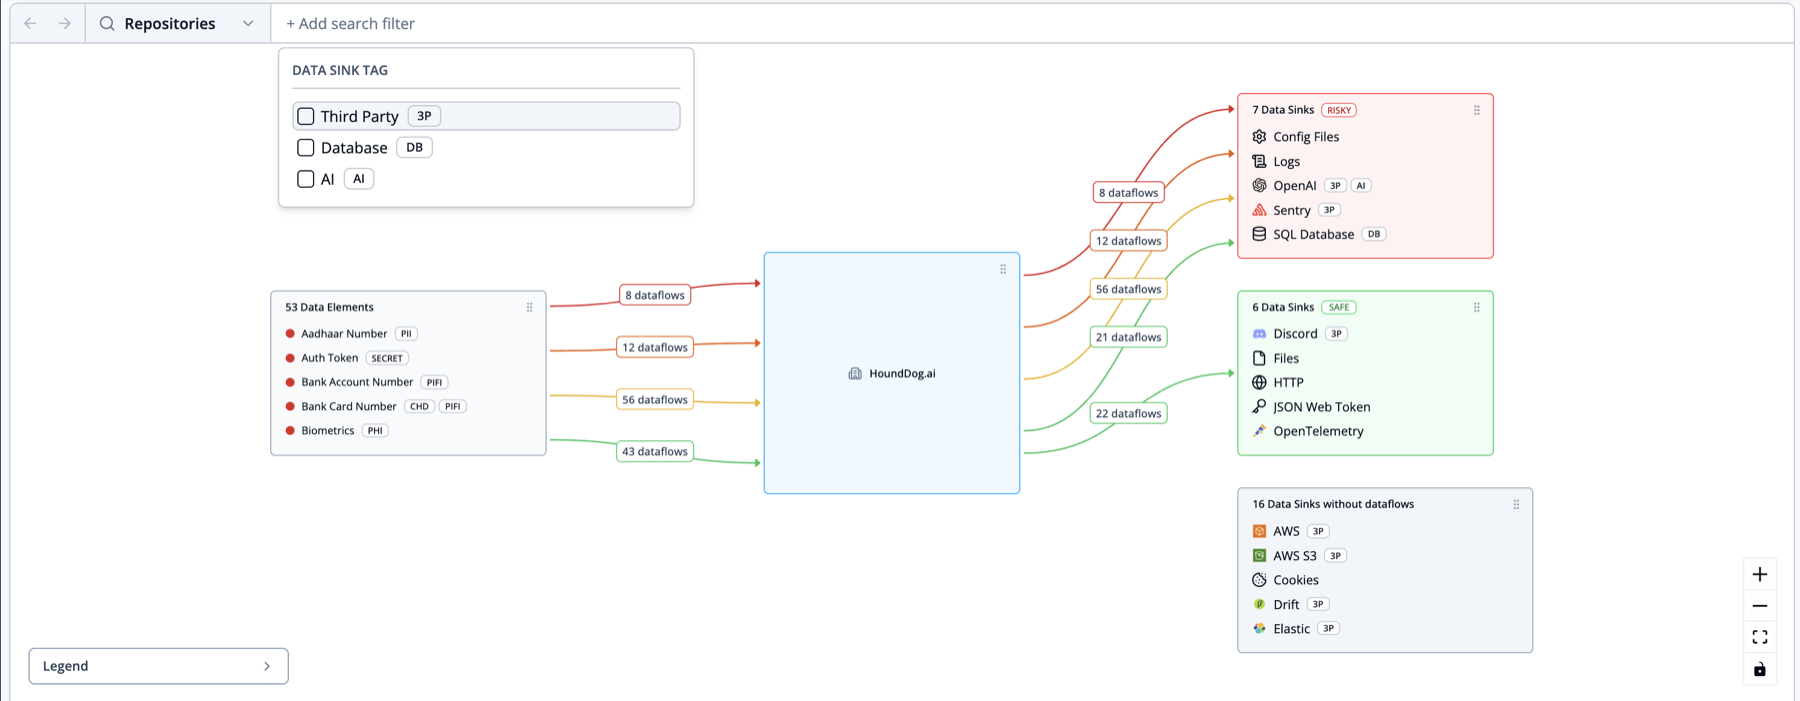
Sensitive data exposures to third parties are rarely intentional; they happen as codebases grow. A developer prints a full user object, or a tainted variable carries PII through a chain of transformations, and by the time anyone notices, the data has already been sent to a third party. HoundDog.ai traces every flow into every SDK, API, and AI integration in code, so Data Processing Agreement violations are caught at scan time, before any data leaves your application.
For Privacy Teams
At development speed. Catch Data Processing Agreement violations in code before data starts flowing, with privacy teams in control: the engine proposes, the DPO approves.
All third-party and AI integrations detected directly in source code, including Shadow AI, whether the data flows through an SDK or API, with 1,000+ integrations covered out of the box.
Trace 100+ sensitive data types (PII, PHI, CHD, auth tokens) across code paths into logs, storage, APIs, and third-party and AI integrations.
Keep your RoPA updated as new categories of personal data and subprocessors are introduced, detected directly from source code.
Validate design-phase privacy reviews with code-based evidence before code is pushed to production.
Suggest
Org RoPA updates
Verify
Alignment with PIA
Block
Risky data flows
Catch
Log leaks early
Asking questions in plain English
With the self-hosted or cloud platform, your organization’s data map becomes queryable in plain English.
An AppSec engineer asks which sensitive data and auth tokens are leaking into application logs.
Show me all sensitive data and auth tokens leaking in application logs
New chat
Show me all sensitive data and auth tokens leaking in application logs
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
A privacy engineer asks which third-party integrations receive PII.
Which third parties receive PII?
New chat
Which third parties receive PII?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
An AI governance team asks which AI integrations exist and what sensitive data reaches them.
Which AI services receive sensitive data in our code?
New chat
Which AI services receive sensitive data in our code?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
main branch of the hounddogai/hounddog-test-python repository, in one file.Dataflows: one confirmed dataflow, and it is risky.
Without AI, the Datamap is still available, built from the scanner’s deterministic findings. You can apply the same advanced filters to search for dataflows; there is no chat panel and no AI review.
Read the Datamap docs Related: Data Flow MappingRoPAPrivacy Impact AssessmentAI GovernancePrivacy Code Scanning
Static analysis discovers. AI reasons. MCP delivers.
HoundDog.ai is built to make your AI more effective, not to replace it.
The scanner discovers every sensitive dataflow, so your AI tokens go to reasoning over detected flows: assessing risk, triaging dataflows and answering questions about your datamap.
The same commit always produces the same dataflows. Every engineer, privacy reviewer and agent gets the same answer about where sensitive data goes, instead of output that varies with the prompt.
The Rust scanner runs in CI on standard CPU infrastructure, across every repo and every commit, with negligible impact on build times.
Questions
A Data Processing Agreement is a contract between a data controller and a data processor that defines exactly which categories of personal data may be shared, for what purpose, and under what safeguards. Most third-party vendors (analytics, observability, CRM, AI APIs) act as processors, and your DPA with each one sets the boundary on what your code is contractually allowed to send them.
HoundDog.ai traces every sensitive data element across function calls, transformations, and SDK invocations to detect when data not permitted under a DPA reaches a third-party sink such as Datadog, Salesforce, OpenAI, or any other processor. It runs on pull requests and in CI so violations are caught before code is merged.
Yes. You can define a per-vendor allowlist of permitted data elements that mirrors the DPA, and HoundDog.ai will block pull requests that try to send anything outside that allowlist. Different vendors can carry different allowlists, so Datadog can be limited to metadata while Salesforce is allowed contact fields but not SSN.
Yes. AI integrations are first-class third-party sinks. HoundDog.ai traces tainted variables flowing into prompt templates and LLM calls, so PII that ends up inside an OpenAI or Anthropic prompt is flagged the same way as PII written to an analytics SDK.
Proxies, gateways, and DLP act in transit or after the fact, once sensitive data is already moving. They cannot prevent a developer from collecting data that should never have been collected. HoundDog.ai works at the code layer before the data starts flowing, which is the only place to enforce true data minimization.
See it in action
A short walkthrough of how HoundDog.ai discovers third-party integrations, traces sensitive data flows to each one, and surfaces unsafe flows in the pull request before they ship.
Try the free Privacy Code Scanner and see exactly which data elements reach each SDK, API, and AI integration, before your DPAs are violated.