Privacy Code Scanner
Trace every PHI flow directly in your application's source code to satisfy HIPAA 164.308(a)(1)(ii)(B) risk analysis, 164.312(b) audit controls, and 164.314(a)(2) business associate oversight, before code is ever pushed to production.
The Problem
PHI exposures to risky data sinks like logs, third-party services, and AI integrations are rarely intentional; they happen as codebases grow.
A snapshot of a system that no longer exists.
No code-level view, no real audit trail.
Contract in place, controls missing.
Code in development
patient = get_patient(id)prompt = f"...{patient.history}"llm.invoke(prompt)BAA violation zone
The result
For Privacy Teams
At development speed. Catch PHI flows that break Business Associate Agreements before code ships, with privacy teams in control: the engine proposes, the DPO approves.
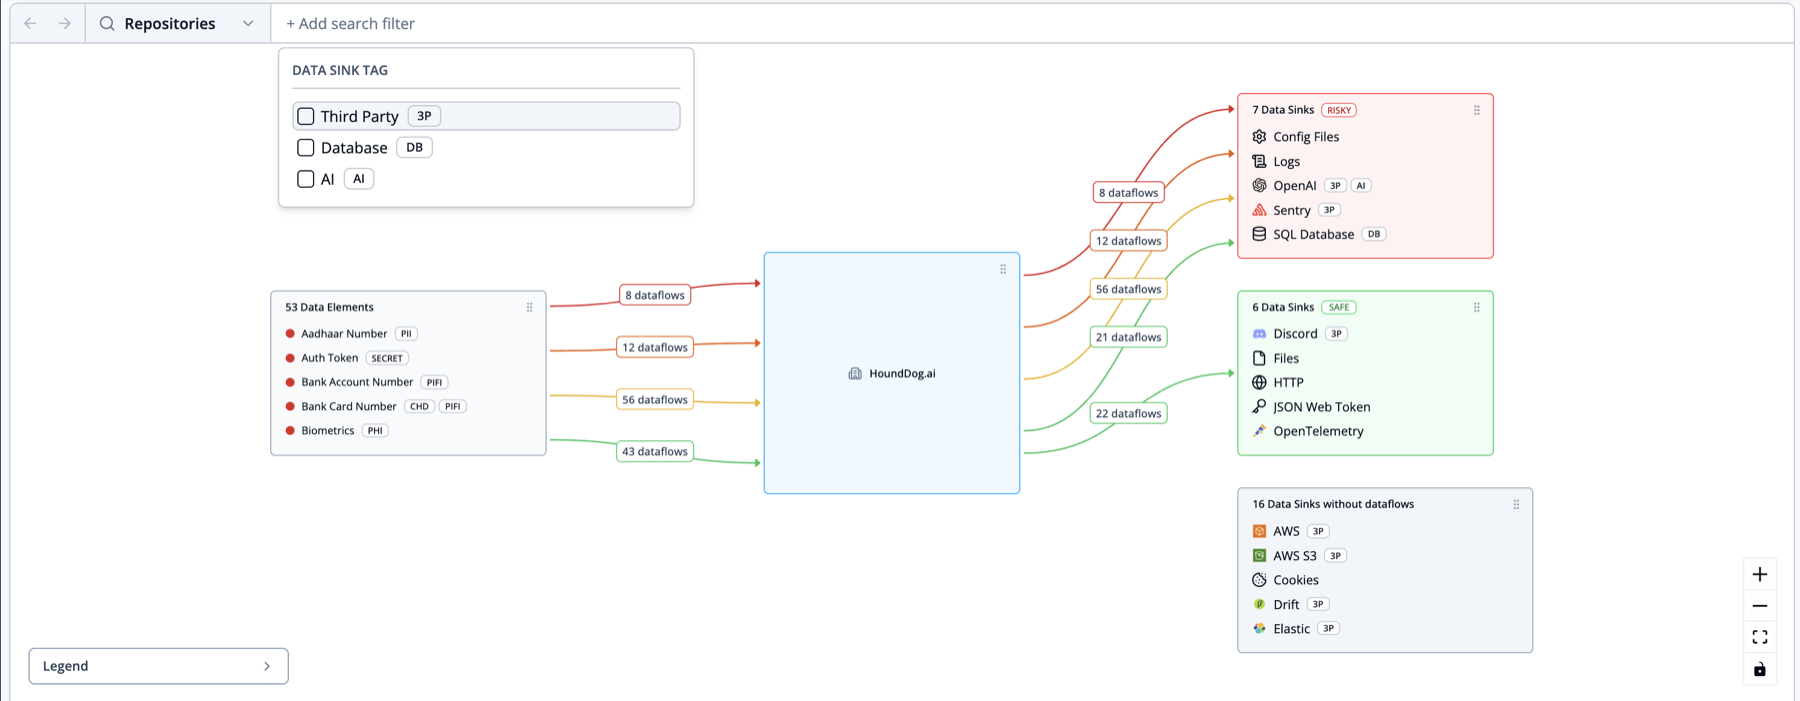
All third-party and AI integrations detected directly in source code, including Shadow AI, whether the data flows through an SDK or API, with 1,000+ integrations covered out of the box.
Trace 100+ sensitive data types (PII, PHI, CHD, auth tokens) across code paths into logs, storage, APIs, and third-party and AI integrations.
Keep your RoPA updated as new categories of personal data and subprocessors are introduced, detected directly from source code.
Validate design-phase privacy reviews with code-based evidence before code is pushed to production.
Suggest
Org RoPA updates
Verify
Alignment with PIA
Block
Risky data flows
Catch
Log leaks early
HIPAA Rules in Code
Risk analysis, audit controls, and business associate oversight: three Security Rule provisions where the textbook answer breaks once real code ships. Here is what changes when evidence comes from the codebase.
Accurate risk assessment of every ePHI flow across the system.
Mechanisms to record and examine activity in systems that handle ePHI.
Business associate contracts and satisfactory assurances PHI is safeguarded.
Asking questions in plain English
With the self-hosted or cloud platform, your organization’s data map becomes queryable in plain English.
An AppSec engineer asks which sensitive data and auth tokens are leaking into application logs.
Show me all sensitive data and auth tokens leaking in application logs
New chat
Show me all sensitive data and auth tokens leaking in application logs
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
A privacy engineer asks which third-party integrations receive PII.
Which third parties receive PII?
New chat
Which third parties receive PII?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
An AI governance team asks which AI integrations exist and what sensitive data reaches them.
Which AI services receive sensitive data in our code?
New chat
Which AI services receive sensitive data in our code?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
main branch of the hounddogai/hounddog-test-python repository, in one file.Dataflows: one confirmed dataflow, and it is risky.
Without AI, the Datamap is still available, built from the scanner’s deterministic findings. You can apply the same advanced filters to search for dataflows; there is no chat panel and no AI review.
Read the Datamap docs Related: Data Flow MappingRoPAPrivacy Impact AssessmentAI GovernanceDPA EnforcementPrivacy Code Scanning
Static analysis discovers. AI reasons. MCP delivers.
HoundDog.ai is built to make your AI more effective, not to replace it.
The scanner discovers every sensitive dataflow, so your AI tokens go to reasoning over detected flows: assessing risk, triaging dataflows and answering questions about your datamap.
The same commit always produces the same dataflows. Every engineer, privacy reviewer and agent gets the same answer about where sensitive data goes, instead of output that varies with the prompt.
The Rust scanner runs in CI on standard CPU infrastructure, across every repo and every commit, with negligible impact on build times.
FAQ
HoundDog.ai performs static analysis on source code to map every PHI data flow across storage, logs, third-party integrations, and AI services. This produces a continuously updated risk surface that satisfies the periodic risk analysis requirement of HIPAA 164.308(a)(1)(ii)(B) using actual processing behavior, not interview-based estimates.
HIPAA 164.312(b) requires audit controls over PHI. HoundDog.ai builds a code-level inventory of every place PHI is read, written, and forwarded, and flags PHI reaching unintended sinks like logs or files before code ships. The result is a continuous, evidence-backed trail that maps to audit control requirements and shrinks the storage footprint of PHI.
HIPAA 164.314(a)(2) requires that PHI sharing with business associates is limited to what is permitted by the BAA. HoundDog.ai detects every third-party SDK and API call in code, traces which PHI elements flow into each one, and lets you define a per-vendor allowlist that fails the pull request when an unapproved PHI element is added.
No. HoundDog.ai runs entirely on source code in your development environment or CI pipeline. It never needs production access, never sees actual PHI, and never sends source code off your machine.
Yes. HoundDog.ai recognizes direct and indirect AI SDKs including OpenAI, Anthropic, LangChain, and LlamaIndex, and traces which PHI fields end up inside prompts or model inputs before the call ever executes in production.
Trace every PHI flow before it ships, shrink the storage footprint of patient data, and keep your BAA inventory honest with evidence pulled directly from source.