Automate GDPR Data Mapping and Privacy Risk Prevention Before Deployment With Final Privacy Checks in Your CI Pipeline

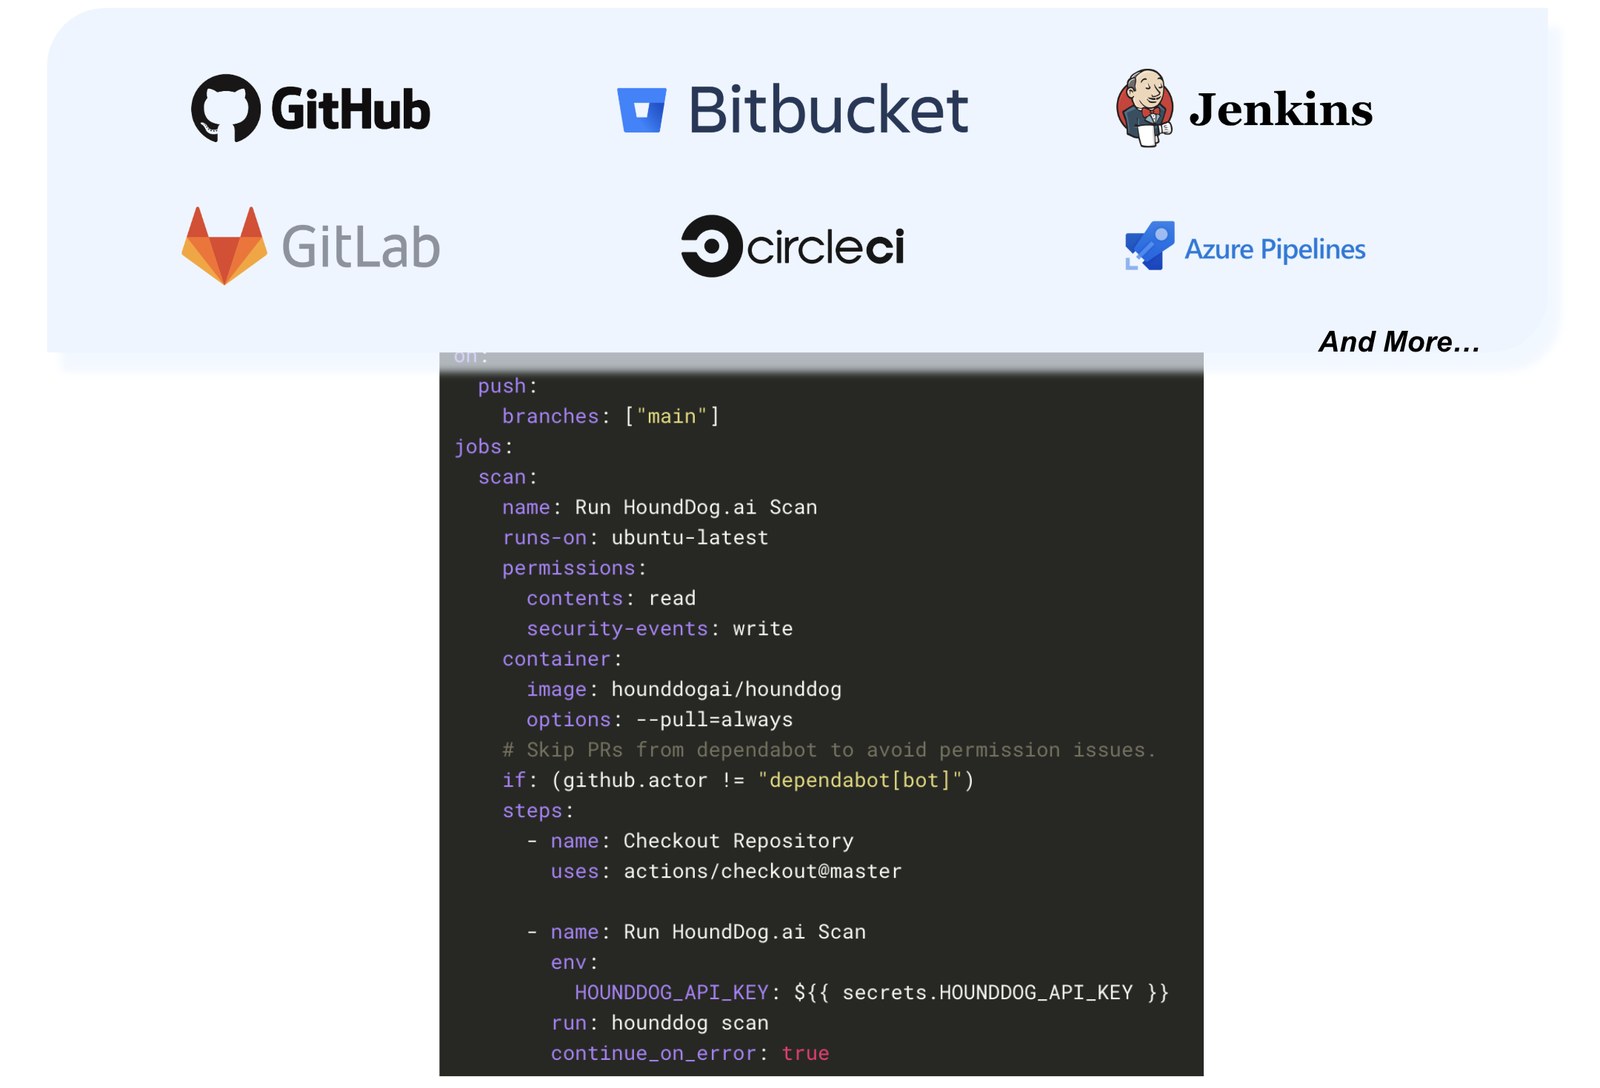
Run sensitive data flow scans on every pull request across GitHub, GitLab, Bitbucket, Jenkins, CircleCI, Azure Pipelines, and others. Block builds when critical privacy leaks land and give developers actionable feedback directly in their code review.

HoundDog.ai CI integrations: GitHub, GitLab, Bitbucket, Jenkins, CircleCI, Azure Pipelines, with example YAML scan configuration

Roll Out CI Scans Across Thousands of Repos in Minutes, Not Months

For enterprises with thousands of repositories that prefer running scans in their own CI workflows, configuring CI across every codebase by hand can take months of engineering effort. With HoundDog.ai, it becomes a five-minute task.

Add CI job configuration files to hounddogai/hounddog-test-healthcare-app, as a pull request
Pull request scans Run scans when merge or pull requests are created or updated. Comments with fixes Comment on pull requests with remediation guidance and code suggestions. Periodic scans Scan the default branch on a schedule. Build blocking Fail the build on findings at or above the severity threshold. Severity thresholdHigh ⌄ Runnerprod-us-east-1-ubuntu-arm64 ⌄ Cancel Preview CI files .github/workflows/hounddog.yml ready to open as a pull request

Push Tailored CI Configurations Directly From the HoundDog.ai Cloud Platform

The HoundDog.ai Cloud Platform integrates with your source management platform (GitHub, GitLab, and Bitbucket, cloud and enterprise editions) and pushes tailored CI configurations as direct commits or pull requests requiring approval.

Each configuration lets you customize scan frequency, pull request blocking logic, developer feedback as actionable comments in pull requests, and cloud-hosted or self-hosted runners.

Integrations Supporting Most CI Pipelines

HoundDog.ai's Privacy Code Scanner integrates directly with your CI/CD pipelines, giving every repository a pre-merge privacy check.

Org-Wide Coverage

Push tailored CI configurations to every selected repository from one place, with no per-team YAML to maintain.

Learn more

CI/CD Integrations

Run continuous scans on every pull request before code is merged into the main branch.

Setup instructions

From Baseline Scan to Continuous Coverage

Most organizations start with a baseline scan, then progress toward continuous privacy coverage.

  1. 1

    Baseline CLI Scan

    Run HoundDog.ai locally against your most critical repositories to establish a baseline and prioritize urgent sensitive data leaks.

  2. 2

    Org-Wide CI/CD Integrations

    Connect your source manager and push HoundDog.ai into every selected repository's CI pipeline as a pre-merge gate, with build blocking on critical findings and inline comments on pull requests.

Make Privacy by Design a Reality in Your SDLC

Shift left on privacy with code scanning. Detect sensitive data leaks, map sensitive data flows, surface suggested RoPA updates backed by code-based evidence, and generate PIA and DPIA before code reaches production.