Privacy Code Scanner
A privacy code scanner that helps privacy and engineering teams detect PII leaks, trace sensitive data flows, and automate GDPR data mapping while code is being written, not after apps are live. If your app uses AI, APIs, or third-party integrations, traditional privacy tools are already too late.
The Problem
Traditional privacy tools detect problems too late, when data is already in motion, pushing teams into remediation rather than prevention.
Works at 10 apps. Breaks at 1,000.
Ships the template, not the data flows.
Looks at production. Never at the code.
The result
Use Cases
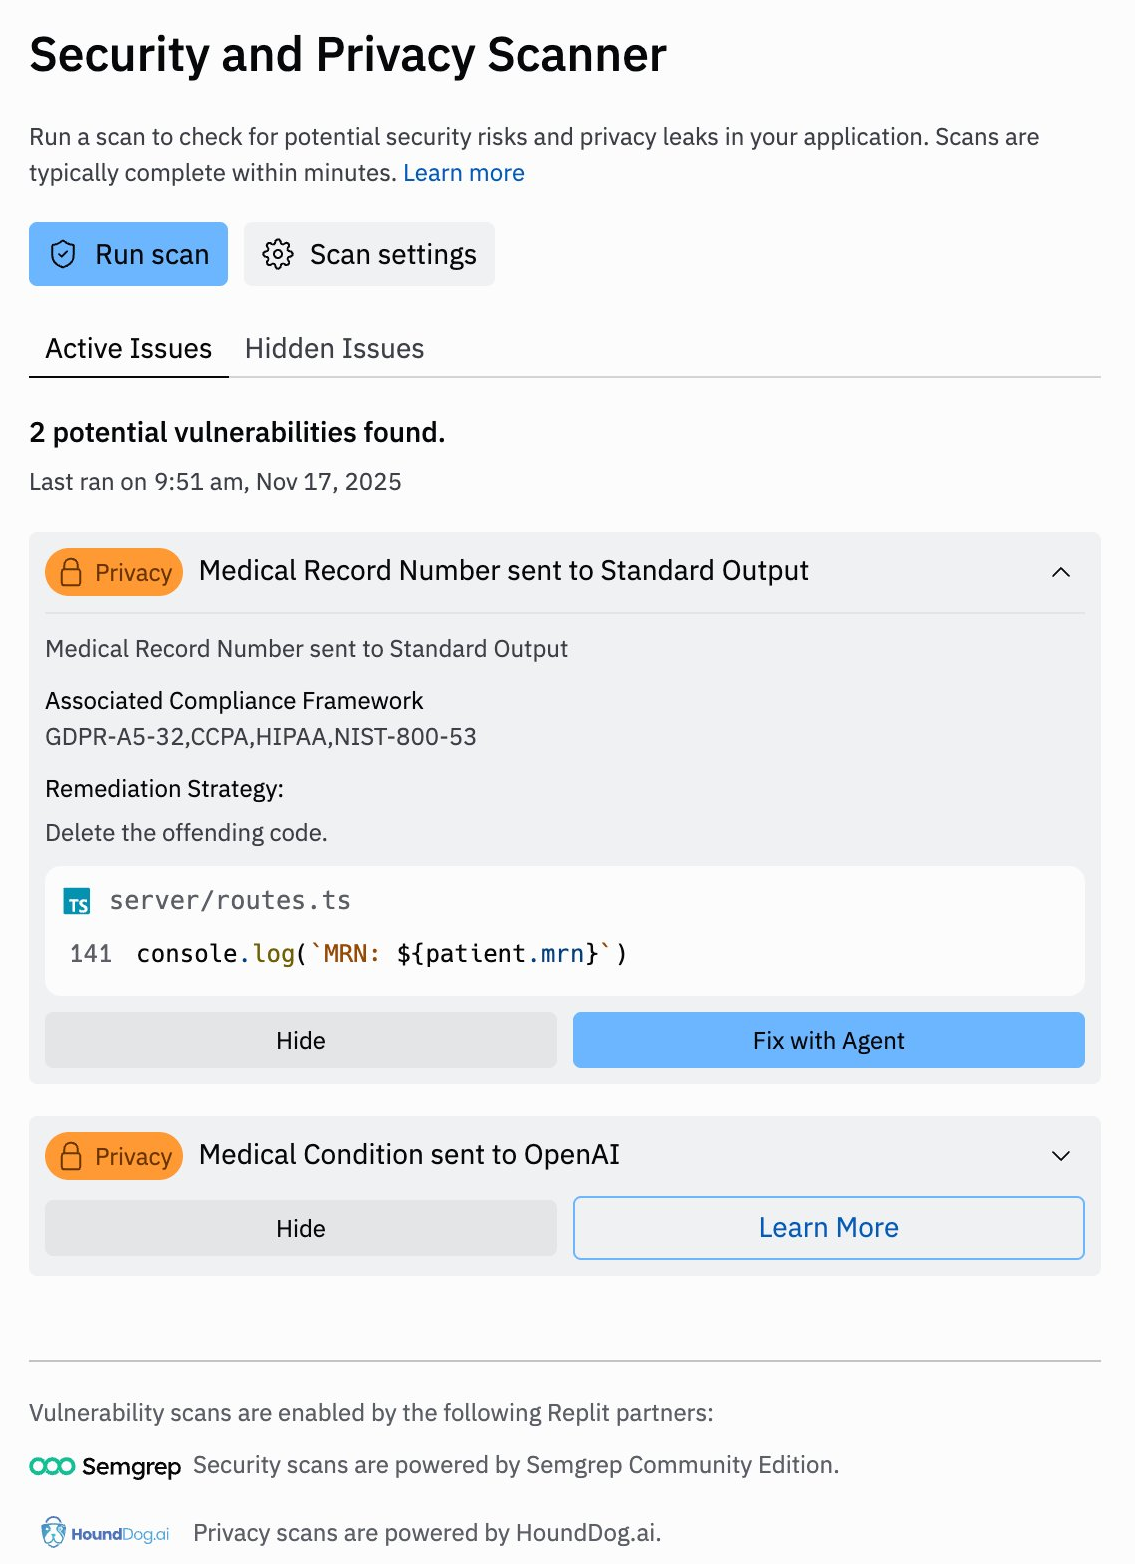
Catch leaks into application logs and other risky mediums before they reach production.
Learn moreDiscover AI integrations and see exactly what types of data are shared with them.
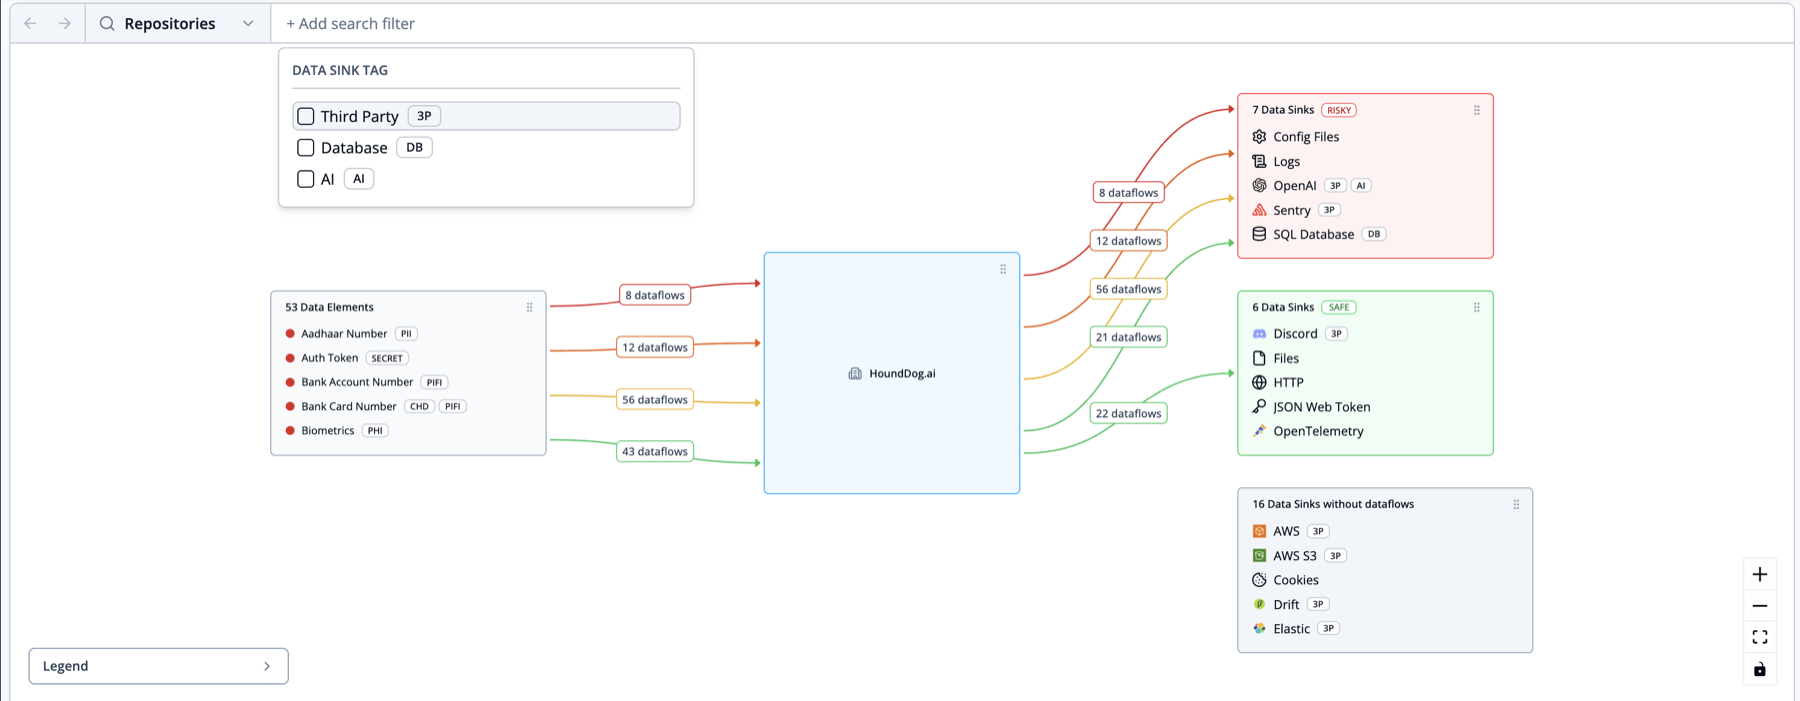
Learn moreGive privacy teams deterministic evidence of actual data flows so they can prevent risks instead of documenting them after the fact.
Learn moreReflect new categories of personal data and subprocessors as developers introduce them, instead of lagging one or two quarters behind the code.
Learn moreAsking questions in plain English
With the self-hosted or cloud platform, your organization’s data map becomes queryable in plain English.
An AppSec engineer asks which sensitive data and auth tokens are leaking into application logs.
Show me all sensitive data and auth tokens leaking in application logs
New chat
Show me all sensitive data and auth tokens leaking in application logs
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
A privacy engineer asks which third-party integrations receive PII.
Which third parties receive PII?
New chat
Which third parties receive PII?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
An AI governance team asks which AI integrations exist and what sensitive data reaches them.
Which AI services receive sensitive data in our code?
New chat
Which AI services receive sensitive data in our code?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
main branch of the hounddogai/hounddog-test-python repository, in one file.Dataflows: one confirmed dataflow, and it is risky.
Without AI, the Datamap is still available, built from the scanner’s deterministic findings. You can apply the same advanced filters to search for dataflows; there is no chat panel and no AI review.
Read the Datamap docs Related: Data Flow MappingRoPAPrivacy Impact AssessmentAI GovernanceDPA Enforcement
Static analysis discovers. AI reasons. MCP delivers.
HoundDog.ai is built to make your AI more effective, not to replace it.
The scanner discovers every sensitive dataflow, so your AI tokens go to reasoning over detected flows: assessing risk, triaging dataflows and answering questions about your datamap.
The same commit always produces the same dataflows. Every engineer, privacy reviewer and agent gets the same answer about where sensitive data goes, instead of output that varies with the prompt.
The Rust scanner runs in CI on standard CPU infrastructure, across every repo and every commit, with negligible impact on build times.
Flagship deployment
Detect PII leaks, map sensitive data flows, generate GDPR data maps, PIA, and DPIA, and keep your RoPA current, before code reaches production.