Fortune 1000 enterprises trust HoundDog.ai across engineering and privacy

Customers use ProtoMap to ship cross-service changes faster with deterministic API context, and the Privacy Code Scanner to detect PII leaks, automate GDPR data mapping, and strengthen compliance maturity across GDPR, SCF, HIPAA, PCI, and FedRAMP.

Trusted by

  • Replit
  • Labcorp
  • Wintrust
  • Senseonics
  • Juvare

“For companies handling sensitive data, HoundDog.ai is a real must-have. The scanner is blazingly fast and integrates seamlessly with our GitLab workflow. More importantly, it provides the peace of mind we need by ensuring that sensitive data does not accidentally leak into logs, files, or third-party systems, even with high-frequency updates to the codebases.”

Juvare CISOJuvare

Cost of the gap vs. cost of closing it.

Cost of the gap
~100 hrs
per log-leak incident: scrubbing logs, auditing access, halting SIEM ingestion.
6,000+ hrs
a year on manual remediation at five leaks a month.
3 months
average documentation lag, a quarter behind the code.
Value with HoundDog.ai
90%
less manual data-mapping effort (Fortune 500 outcome).
$2M
saved by one customer in eng hours and masking tooling.
< 5 min
to remediate a flagged exposure, fix suggested in the PR.
$200 / developer / year

Flat per-scan cost. No token meter, predictable in CI, a fraction of a single remediation cycle, and it prevents the incident instead of cleaning it up.

Book a Demo

HoundDog.ai + Replit

50M
Users protected
100k
Scans daily
100+
Data types
  • Detects leaks before publishing. Auth tokens and passwords in logs or local storage, caught at scan time.
  • Flags unscoped AI & third-party flows. PII/PHI to integrations that don't match published privacy notices.
  • Privacy by default, not retrofit. AI-generated apps embed GDPR & CCPA best practices from day one.
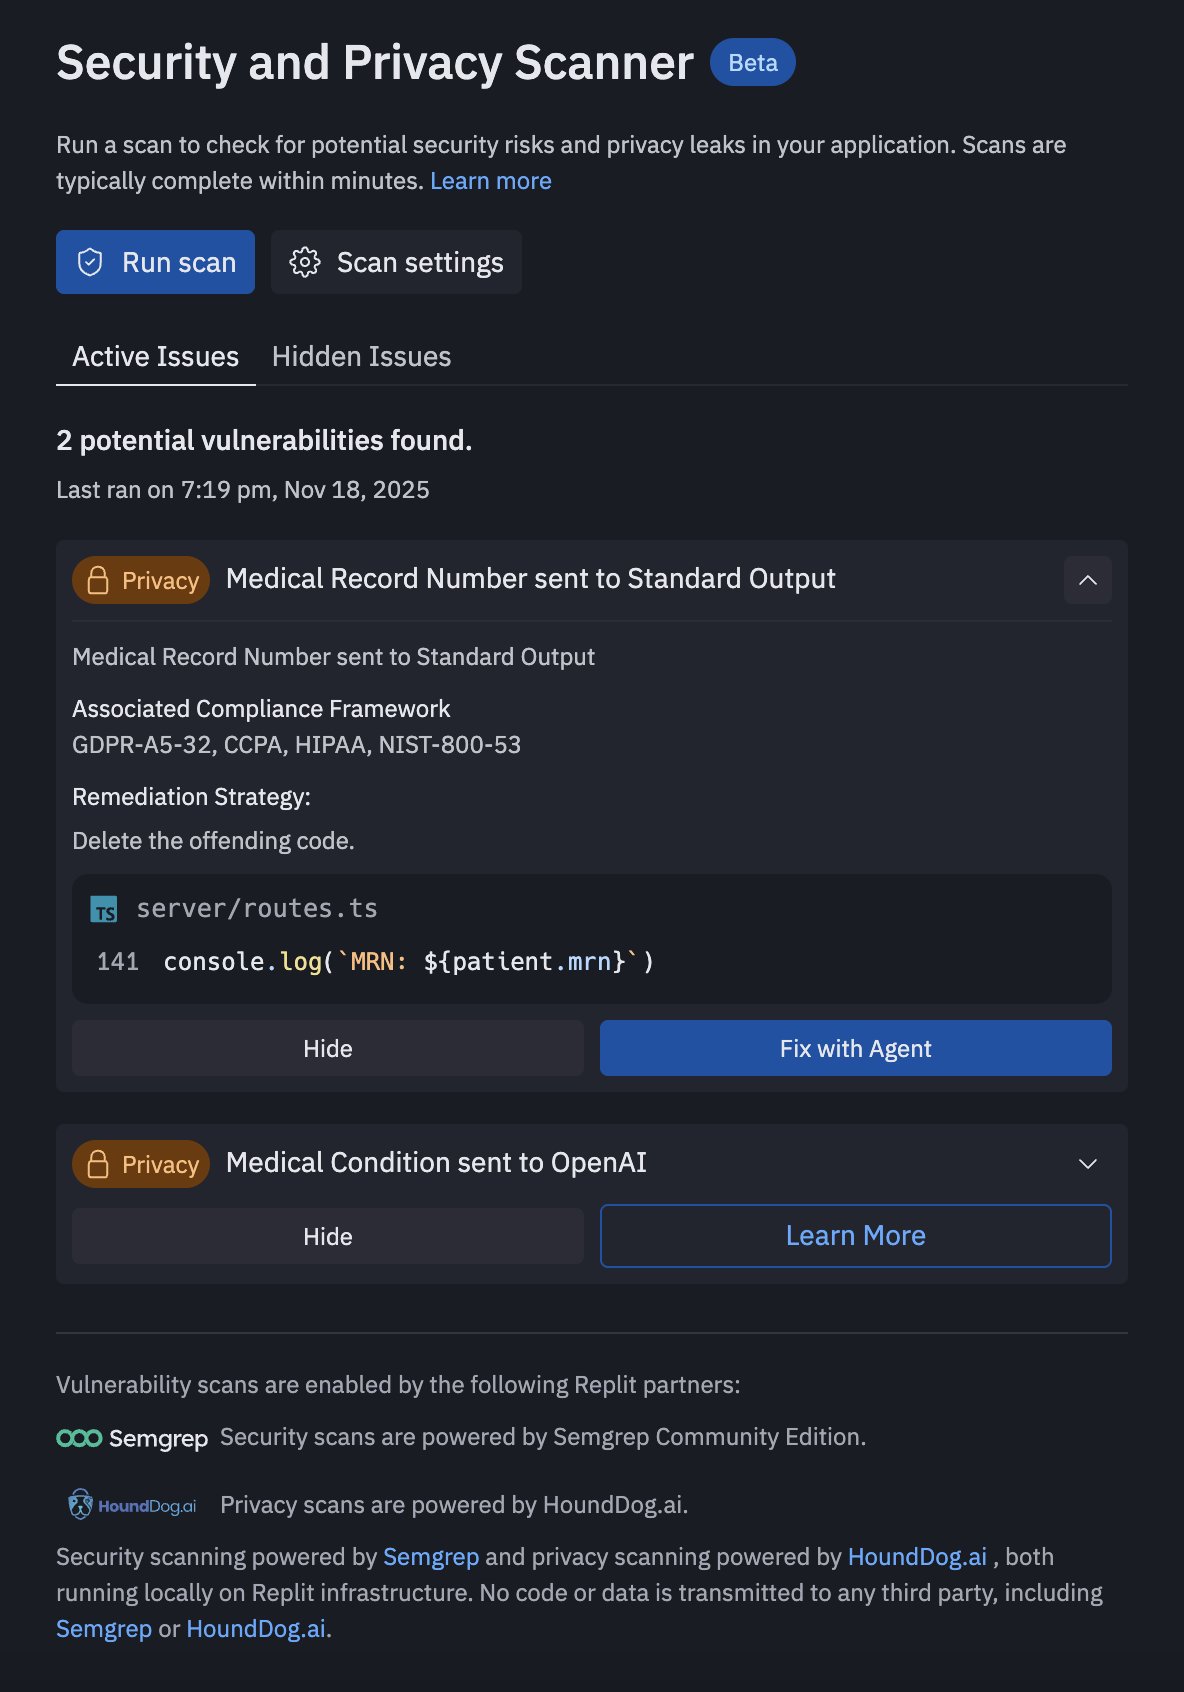
Replit Security and Privacy Scanner, powered by HoundDog.ai, flagging a Medical Record Number sent to standard output and a Medical Condition sent to OpenAI, with GDPR, CCPA, HIPAA, and NIST-800-53 compliance tags

What teams find in their codebases.

Fortune 500 · Healthcare 90%

less manual data mapping. Automated reporting across 15,000 repos and stronger HIPAA compliance.

Unicorn · Fintech $2M

saved. PII leak incidents cut from five a month to zero across 500 repos.

Public · Travel & Expense ~30%

of AI integrations were Shadow AI, some without a DPA. Now flagged as suggested RoPA edits.

Publicly-listed travel & expense management company.

The HoundDog.ai privacy code scanner surfaced excessive sensitive data leaks in their application logs and identified third-party subprocessors missing from their published Trust Center. Such exposures are rarely intentional: they accumulate over years of development, as codebases, dependencies and data transformations grow. A developer logs a full user object, a tainted variable carries PII through a chain of transformations, and by the time anyone notices, the data is already in logs or with a third party. A representative cross section of what we found:

High

Credentials in logs

OAuth refresh tokens and third-party API keys written to logs in plaintext. Live credentials replayable by anyone with log access.

High

Government identity in logs

Passport numbers and visa details captured alongside traveler identity. Special-category identity data exposed to log readers.

Medium

PII shared with analytics

Real emails sent to an analytics platform as user IDs. Passenger names, phone-email-UUID combinations, and SMS bodies captured in logs across booking flows. More than 400 distinct email-in-log call sites.

20+ Subprocessors not disclosed

Subprocessor disclosure gap

Of the more than 20 subprocessors with confirmed data flows detected in the source code, only two appeared on the customer's published Trust Center list. AI and LLM providers accounted for most of the gap, highlighting how privacy documentation often lags behind active development. Some AI subprocessors, including orchestration tools, did not have an established Data Processing Agreement.

GDPR implications

Logged credentials and identity data can violate Articles 5 and 32. Sharing identifiers with analytics tools or Slack without disclosure can create Article 28 and 30 gaps. Exposures may trigger Articles 33 and 34 breach notifications.

From challenges to outcomes.

Unicorn FinTech

200 developers
Challenges
  • PII in logs Appears 1 to 2 times a month, causing interrupt work for SREs. Days, sometimes weeks, are spent scrubbing logs, assessing exposure across tools that ingested them, and patching code after the fact.
  • Costly third-party PII masking Datadog's per-GB scanned pricing is prohibitive, nearing $1M per year for full coverage, and that's just for logs within Datadog.
Outcomes with HoundDog.ai
  • $1M in cost savings Eliminated the need for Datadog's $700K log masking, reduced reliance on AWS Macie for PII detection, and removed the disruptive effort of remediating log leaks, saving an average of 80 hours per incident.
  • PII leak elimination Identified 500+ sensitive leaks, established a baseline across all 500 code repositories scanned, and prioritized the remediation backlog.
  • Automated continuous coverage GitHub App runs on every merge, proactively detecting PII leaks in new code and blocking risky PRs.
Fortune 500 Healthcare

1,000 developers
Challenges
  • Expensive and incomplete detection With thousands of code repositories, relying solely on DLP for PII leaks is costly and lacks third-party coverage.
  • Gaps in SCF compliance Privacy-related controls including data minimization, RoPA, and third-party data sharing are only partially met or addressed reactively.
Outcomes with HoundDog.ai
  • 90% reduction in data-mapping overhead Automated data flow documentation and privacy reporting across thousands of code repositories supplemented existing privacy tools and ended the long manual-correction cycles caused by flows missed in shadow third-party integrations or by frequent code changes.
  • Zero PII leaks Reduced monthly sensitive data leak incidents from 10 to zero across thousands of code repositories by detecting and preventing leaks at the source, before they reached production logs.
  • Enhanced privacy maturity Strengthened HIPAA and privacy program maturity by enabling earlier visibility into data flows, automating data mapping tasks, and reducing exposure in third-party integrations.

The #1 privacy risk hiding in plain sight: your logs.

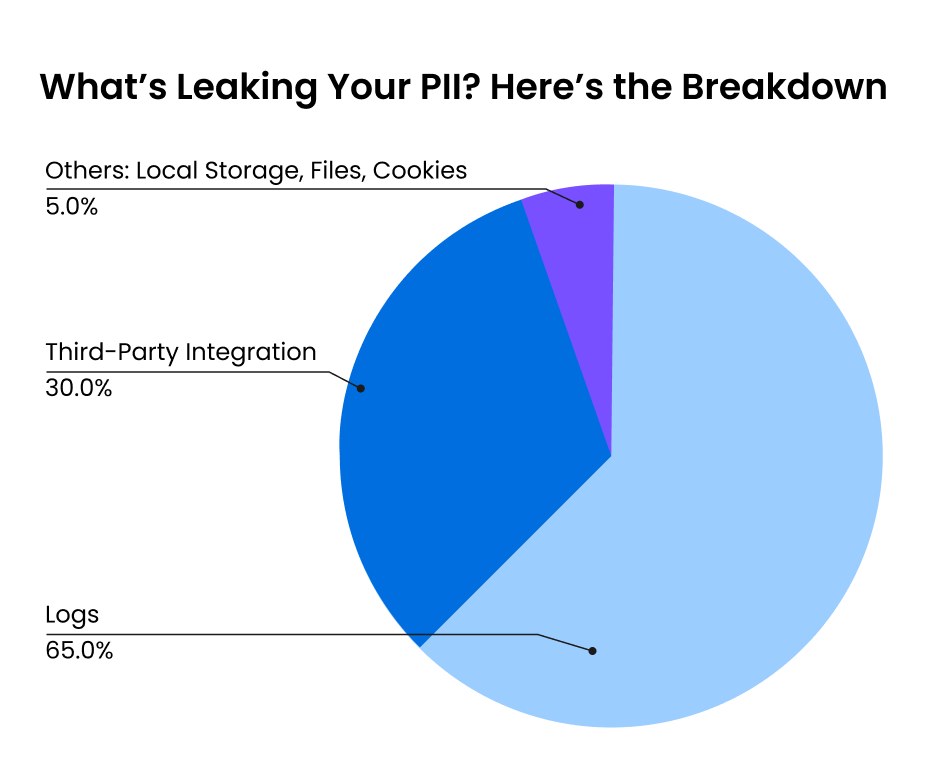
Based on thousands of leaks detected by the HoundDog.ai scanner, logs rank first at 65% of findings, followed by third-party integrations at 30%. Other risky mediums like local storage, files, and cookies make up the remaining 5%.

Logs are among the riskiest mediums: multiple tools ingest them, and they make it easier for attackers already inside your network to exfiltrate data. Relying solely on DLP for PII detection in logs is reactive and unreliable due to sampling limitations, so issues often surface too late, after the logs have spread, without context on the root cause.

Pie chart: What is leaking your PII. Logs 65%, Third-Party Integration 30%, Others 5%
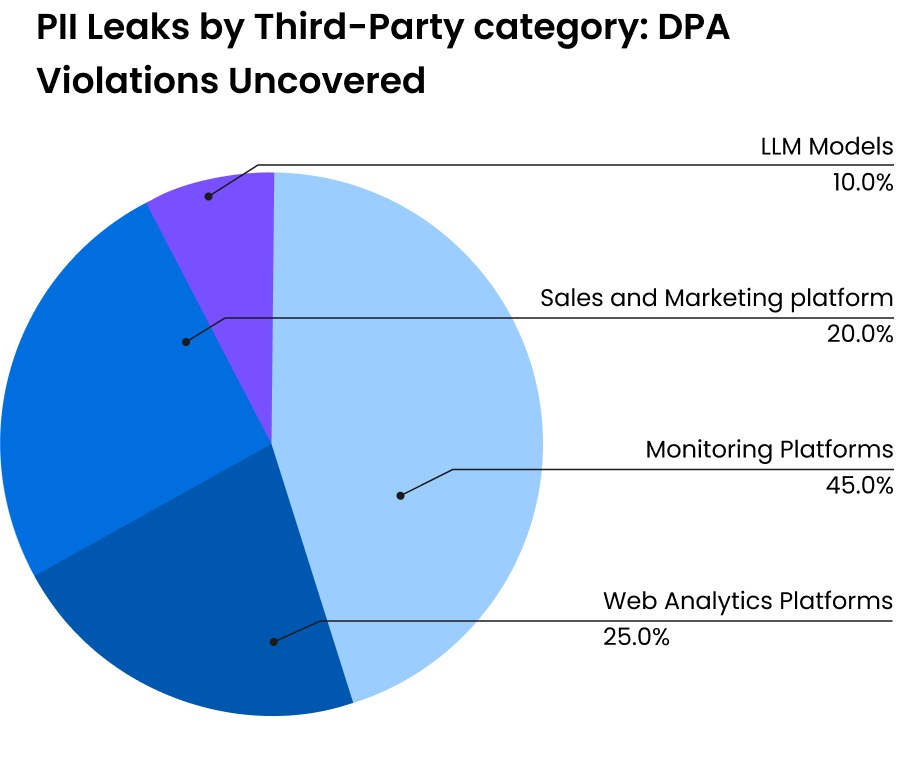
Pie chart: PII leaks by third-party category. Monitoring Platforms 45%, Web Analytics 25%, Sales and Marketing 20%, LLM Models 10%

Monitoring platforms lead. LLMs are growing fast.

Among leaks found in third-party integrations, monitoring platforms like Datadog account for the largest share of PII exposure at 45%, well beyond what is permitted under accepted Data Processing Agreements.

Sales and marketing platforms, web analytics tools, and LLM integrations all lead to DPA violations, and AI models are the fastest-growing PII risk.

Make Privacy by Design a reality and ship faster across services.

Detect PII leaks, automate GDPR data mapping, and give engineers deterministic cross-repo API context, all before code reaches production.