Privacy Code Scanner
Data Flow Mapping
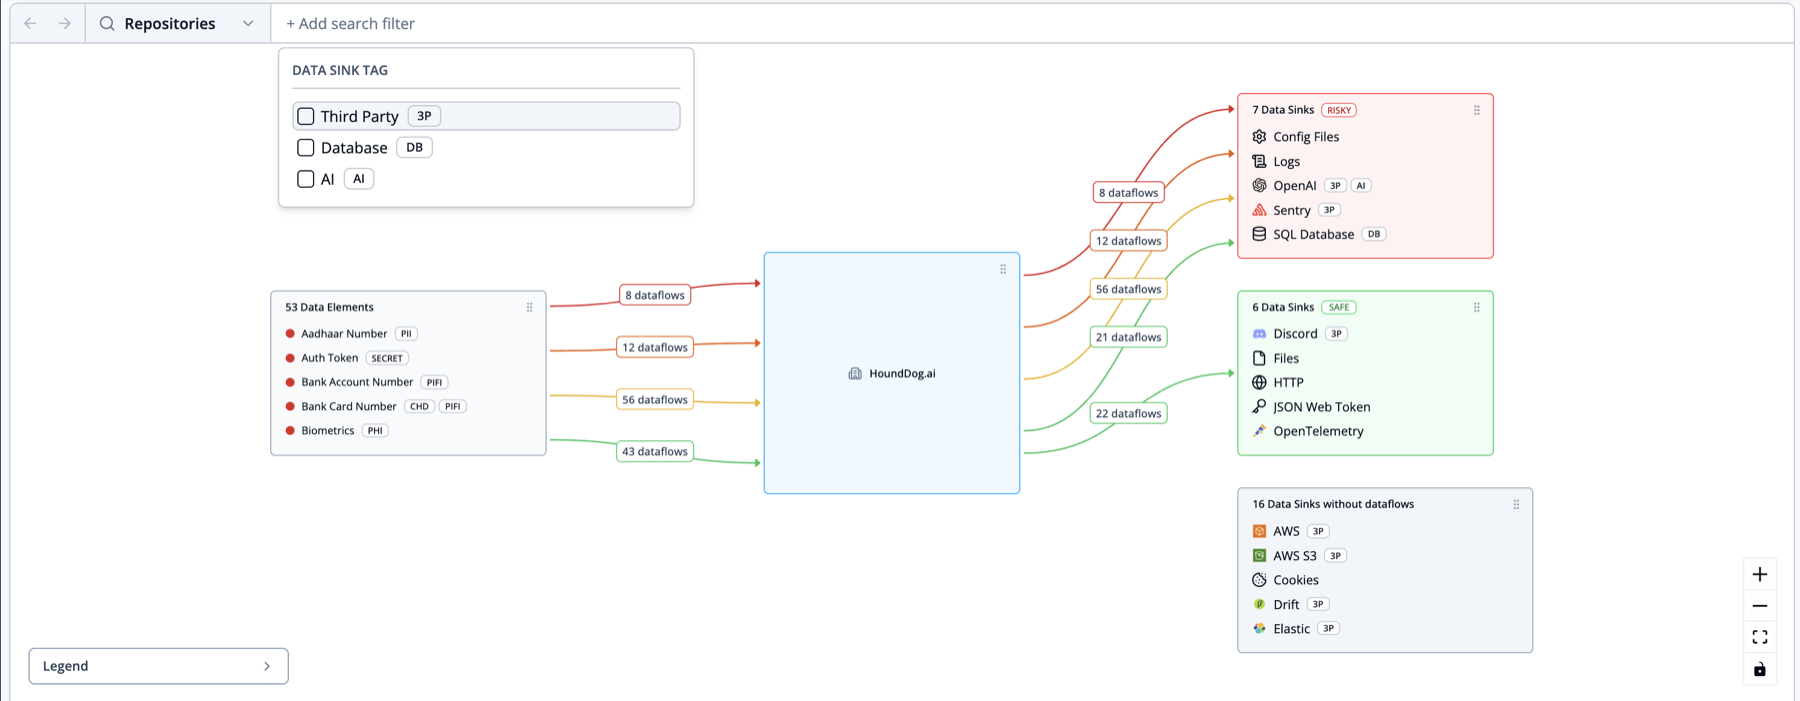
The code logic in your custom applications defines how sensitive data flows across storage, APIs, and third-party and AI integrations. HoundDog.ai maps those flows directly from source code, before production.
The Capability
What Is Data Flow Mapping?
Data flow mapping traces how sensitive data moves through an application, across functions, services, third-party integrations, and AI tools. HoundDog.ai builds the map statically from source code, so it reflects what your applications actually do, not what surveys and diagrams say they do.
What sensitive data is collected
Where that data is stored
How it moves between services, third parties, and AI tools
Whether each flow meets policy and regulatory requirements
Coverage spans every relevant data type:
- Personal and user data
- Customer and account identifiers
- Financial and transactional data
- Protected health information
- Authentication tokens and secrets
- Internal metadata and proprietary fields
Hidden Risk
Data Flows You Can't See in Production Tools
Privacy teams rely on three workflows today, and none of them keeps up with modern development.
Manual Documentation Does Not Scale
- Engineering gets flooded with privacy questionnaires every release
Works at 10 apps. Breaks at 1,000.
GRC Platforms
- Provide blank RoPA, PIA, and DPIA templates, like this one from Vanta, and leave privacy teams to interview engineers and collect data flows by hand
Ships the template, not the data flows.
Privacy Platforms Are Blind to the Codebase
- Privacy platforms infer flows after deployment, missing shadow AI and SDKs added in code
Looks at production. Never at the code.
The result
- Stale Evidence
- Documentation runs months behind the code.
- Drift
- Documented activities drift from code each release.
- Exposure
- Undocumented subprocessors: an Article 30 risk.
Benefits
Why map data flows from code
Identify Where Sensitive Data Actually Lives
In complex applications, sensitive data rarely stays where teams expect it to.
Prevent AI Data Leaks Before They Happen
As AI usage expands, so does the risk of unintentionally sharing sensitive data with external models.
Replace Guesswork with Code-Level Evidence
Because it finds root causes, not just outcomes, teams fix issues permanently instead of chasing recurring alerts.
Stay Audit-Ready by Default
The evidence updates continuously as systems change, so there is no scramble to recreate reality during audits.
Asking questions in plain English
Typical questions come from different teams
With the self-hosted or cloud platform, your organization’s data map becomes queryable in plain English.
An AppSec engineer asks which sensitive data and auth tokens are leaking into application logs.
Show me all sensitive data and auth tokens leaking in application logs
 HoundDog.ai Acme Corp
 New chat
Show me all sensitive data and auth tokens leaking in application logs
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
A privacy engineer asks which third-party integrations receive PII.
Which third parties receive PII?
HoundDog.ai Acme Corp
New chat
Which third parties receive PII?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
An AI governance team asks which AI integrations exist and what sensitive data reaches them.
Which AI services receive sensitive data in our code?
HoundDog.ai Acme Corp
New chat
Which AI services receive sensitive data in our code?
···
Ask HoundDog.ai about your data
Suggested for you
Which repositories handle medical data?Show me the most severe open risky dataflows right nowWhich third parties receive PII?Which AI services receive sensitive data in our code?What data elements are present in my code?
main branch of the hounddogai/hounddog-test-python repository, in one file.Dataflows: one confirmed dataflow, and it is risky.
The same Datamap, built from deterministic findings
Without AI, the Datamap is still available, built from the scanner’s deterministic findings. You can apply the same advanced filters to search for dataflows; there is no chat panel and no AI review.
- By repository — select several, such as backend, frontend, and an authentication service, to see every dataflow across them.
- By data element — “show me every repository where Social Security Number is processed” and every sink it may be exposed to.
- By data sink — “show me all sensitive data sent to OpenAI org-wide.”
Read the Datamap docs Related: RoPAPrivacy Impact AssessmentAI GovernanceDPA EnforcementPrivacy Code Scanning
Static analysis discovers. AI reasons. MCP delivers.
Why not just use an LLM?
HoundDog.ai is built to make your AI more effective, not to replace it.
Tokens for reasoning, not discovery.
The scanner discovers every sensitive dataflow, so your AI tokens go to reasoning over detected flows: assessing risk, triaging dataflows and answering questions about your datamap.
Evidence you can stand behind.
The same commit always produces the same dataflows. Every engineer, privacy reviewer and agent gets the same answer about where sensitive data goes, instead of output that varies with the prompt.
Easy to roll out org-wide.
The Rust scanner runs in CI on standard CPU infrastructure, across every repo and every commit, with negligible impact on build times.
FAQ
Data Flow Mapping Frequently Asked Questions
What is data flow mapping?
Tracing how sensitive data moves through an application: what is collected, where it is stored, how it travels between services, third parties, and AI tools, and whether those flows comply with policy. HoundDog.ai maps flows statically from source code, before production.
What does data flow mapping software do?
It discovers and visualizes sensitive data flows automatically. HoundDog.ai scans code in your CI pipelines, detects more than 100 sensitive data types, traces each to sinks like logs, databases, SDKs, and AI APIs, and rates every flow by severity.
How is data flow mapping different from GDPR data mapping?
Data flow mapping is the technical capability of tracing flows through code. GDPR data mapping is its compliance application: Article 30 records, assessments, and audit evidence. HoundDog.ai connects the two with suggested Org RoPA edits that the privacy team reviews and approves.
Does HoundDog.ai send my source code anywhere?
No. Scans run inside your own CI pipeline. Only scan findings are used to build the data map.
Make Privacy-by-Design a Reality in Your SDLC
Detect PII leaks, map sensitive data flows, and automate GDPR data mapping at the speed of development.