Only 43 percent of regulated organizations are fully PCI DSS compliant, leaving many exposed to data breaches and non-compliance penalties. PCI DSS fines can range from $5,000 to $100,000 per month, depending on the violation's severity and the business's size. High-profile breaches like those at Target and Home Depot cost millions of dollars in settlements and penalties. And most cardholder data leaks do not start with an attacker: they start with a quiet line of code that logs a payment payload or ships card data to an integration nobody reviewed. This article shows how HoundDog helps you avoid these financial and reputational risks by automating data flow monitoring, PII tracking, and third-party risk management at the code level.
Get Control of Data Flows with PCI DSS 1.2 Compliance
Under PCI DSS Requirement 1.2, organizations must map how cardholder data (CHD) and personally identifiable information (PII) move through their systems. The map shows exactly where sensitive data is processed, stored, or transmitted; without it, compliance is hard and protecting data from breaches is harder.
Companies often over-rely on data already collected in production and on network traffic monitoring to map their applications' data flows. At high development velocity, unpushed code changes and their impact on data flows often go undetected, leaving compliance teams reacting to changes, with little or no input on modifications that could lead to violations.
How HoundDog helps
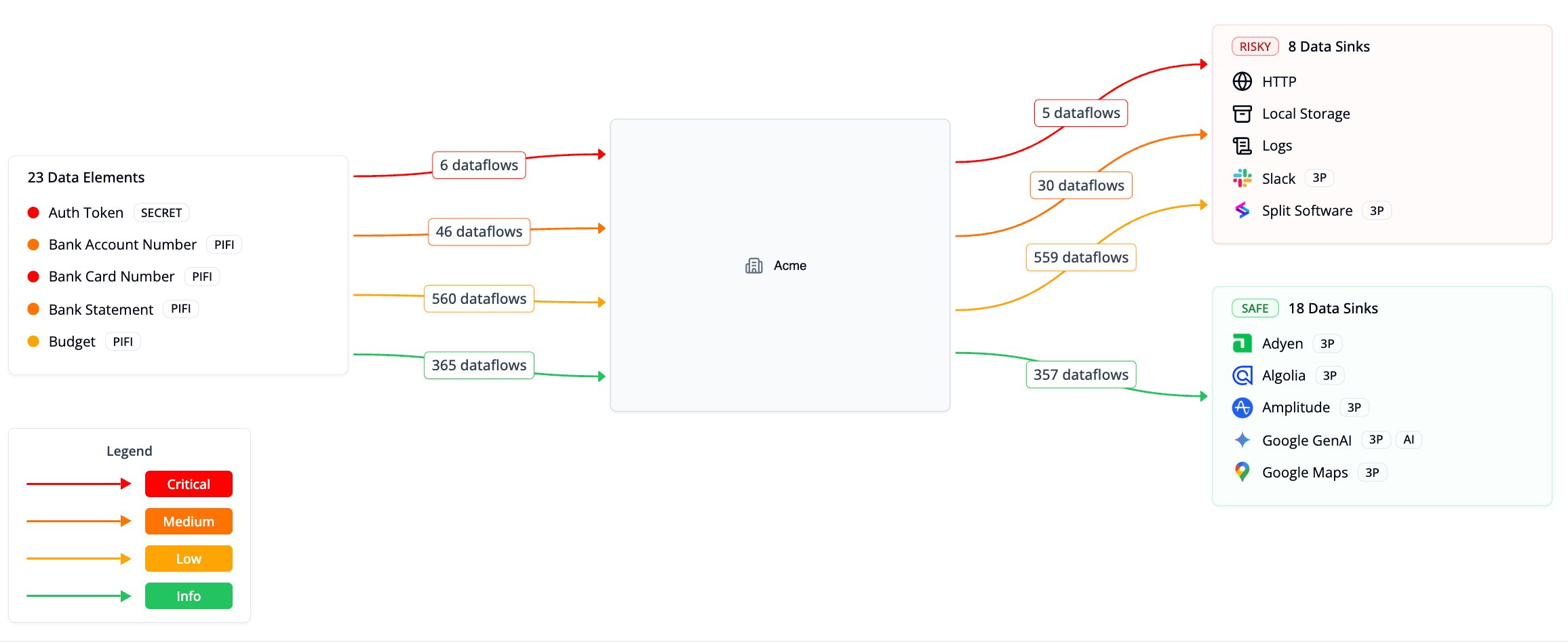
HoundDog keeps you on top of PCI DSS Requirement 1.2 by automating the entire process of mapping data flows. It uses your application's source code as the single source of truth to continuously track how CHD and PII flow through your application, so you always know every storage medium and third-party integration where your sensitive data will end up. All your data flows are monitored before code is pushed to production, including those through third-party processors and complex integrations.
Beyond tracking data, the platform highlights risky or undocumented data flows that might violate PCI DSS, so compliance issues are addressed in development, long before they hit production.
Stop Cardholder Data Leaks into Logs and Files (PCI DSS 3.1)
PCI DSS Requirement 3.1 is about securing stored cardholder data, but many organizations struggle to identify exactly where their PII and CHD is stored, processed, or transmitted, especially as data flows through different systems, tools, and integrations.
The most common failure mode is also the most mundane: a data leak that nobody intended. A developer logs a full request payload while debugging a payment flow, a card number lands in a local storage key, a statement object gets serialized into an error report. None of this is malicious, all of it is invisible to network monitoring until the data is already at rest somewhere it should never be, and every instance expands the scope of your cardholder data environment without anyone deciding it should.
How HoundDog helps
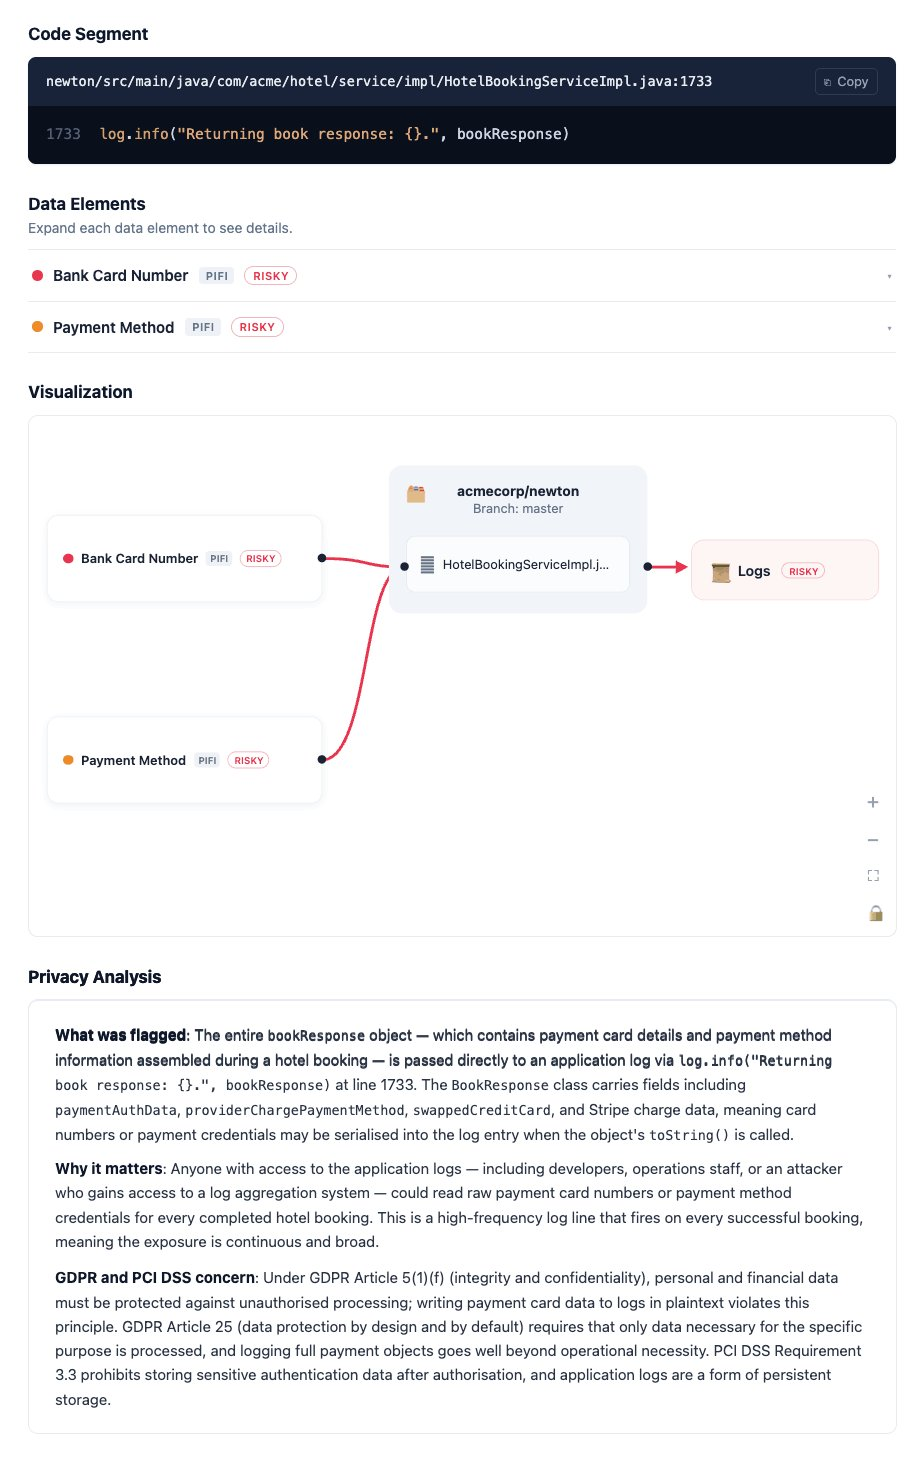
HoundDog's static code scanner continuously tracks PII and CHD exposure across logs, cookies, files, and APIs, with custom allowlists that match your policies. It catches PCI violations caused by unintentional developer mistakes, such as oversharing or overlogging data containing PII or CHD, before the code is pushed to production and the data leak becomes real. Your cardholder data footprint stays limited to where it is supposed to be, keeping you compliant with PCI DSS 3.1.
When it comes to audits, HoundDog keeps your Records of Processing Activities current by surfacing scanner-detected changes as suggested updates to your organization's RoPA, with your privacy team reviewing and approving every edit. All collected, processed, and stored PII stays documented and up to date, so PCI DSS audits are far easier and there is no scramble at audit time.
Reduce Third-Party Risks with PCI DSS 12.8
Under PCI DSS Requirement 12.8, you must monitor and manage all third-party processors to ensure they meet PCI security standards. Whenever you share cardholder data or PII with vendors, it is up to you to ensure they follow the rules.
With many vendors, data-sharing agreements, and services in the data path, it is easy to lose track of how and where data is shared, and that lack of oversight exposes your organization to compliance violations and security risks.
How HoundDog helps
HoundDog continuously monitors the data flowing between your applications and outside services. It shows exactly how CHD and PII are transmitted and shared with third parties, and flags potential compliance risks long before they escalate into production issues.
Your vendor agreements become enforceable policy rather than paperwork: for each payment processor and third-party service, a custom allowlist defines exactly which data elements that vendor is approved to receive. A developer wiring card data into an analytics SDK, or expanding the payload sent to a payment provider beyond what the agreement covers, gets flagged before the code merges, not discovered in an assessment months later.
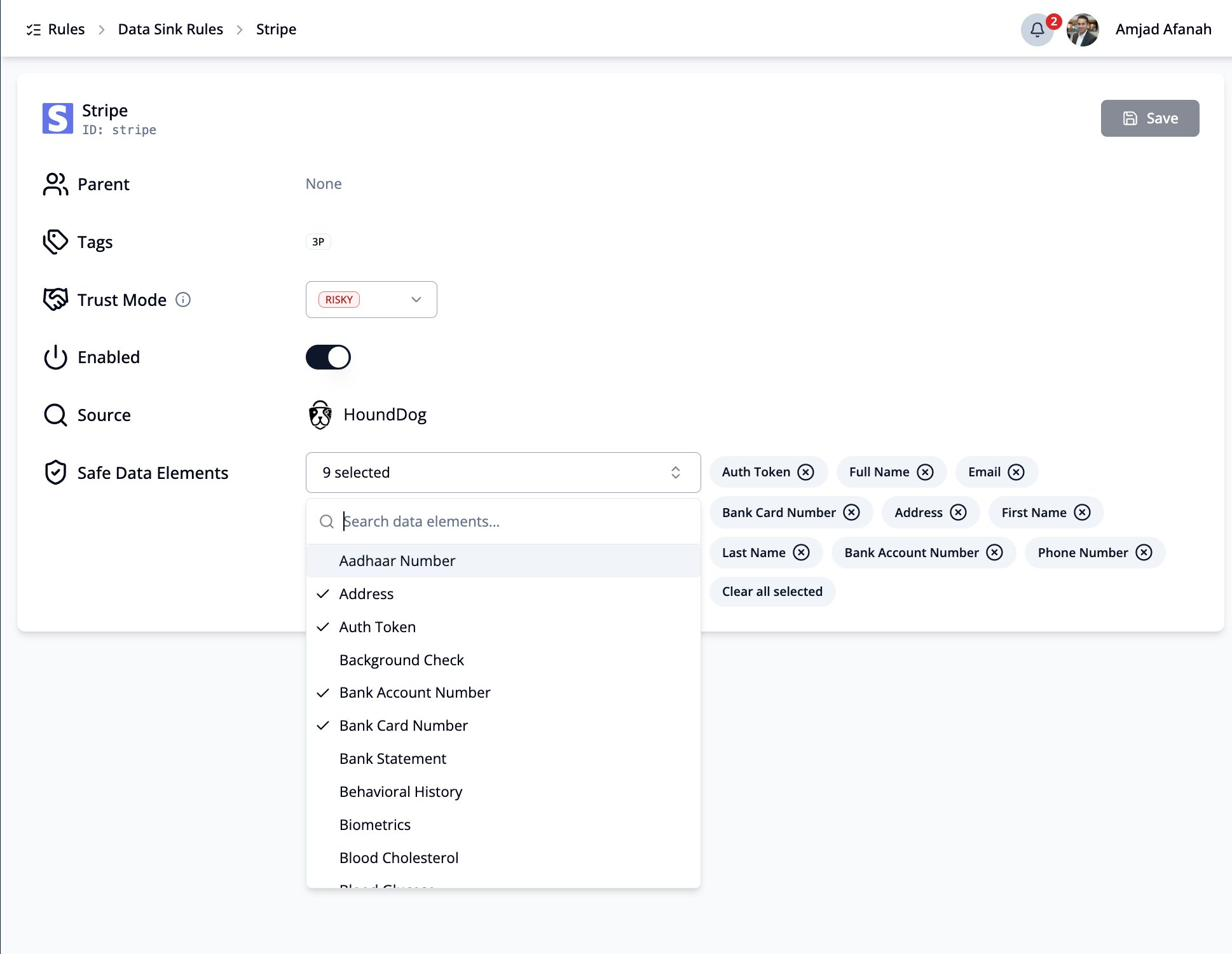
Because third-party risks are caught in development, you avoid emergency fixes and costly remediation, reduce the risk of non-compliance and penalties, and manage third-party relationships with confidence.
Conclusion
We explored how HoundDog automates PCI DSS compliance by tracking data flows (PCI DSS 1.2), preventing cardholder data leaks and managing your PII inventory (PCI DSS 3.1), and monitoring third-party risks (PCI DSS 12.8). These capabilities help you maintain visibility, catch risks early, and stay compliant. To simplify PCI compliance and protect sensitive data, schedule a demo with HoundDog.