The Inspiration Behind This Company
It is a big day for HoundDog.ai. We are coming out of stealth, announcing our Series Seed round of funding and the launch of our platform. Read the announcement.
Before my co-founders and I started HoundDog.ai, I served as the VP of Product at a data security company, specializing in discovering, classifying, and applying access controls to sensitive data in production. There I heard from many security and privacy teams frustrated with reactive data security and privacy measures that could not keep pace with rapid changes in their applications' codebases.
This frustration sparked the idea for HoundDog.ai. Common questions from these teams included:
"How can I prevent PII data from leaking in the first place, rather than catching it once it's already in production logs, files, or third-party systems?"
"How can we establish a reliable method for documenting processing activities that keeps up with changes in our codebase without relying on inconsistent tribal knowledge?"
"How can my privacy engineers stay ahead of product changes that introduce new data collections requiring lawful processing?"
Proactive vs. Reactive Data Security
For too long, organizations have settled for reactive data leak detection and remediation. In 2023, 92% of compromised data involved PII records. Remediating sensitive data leaks can be very expensive, requiring code updates, access log reviews, incident reporting, and, in some cases, customer notifications.
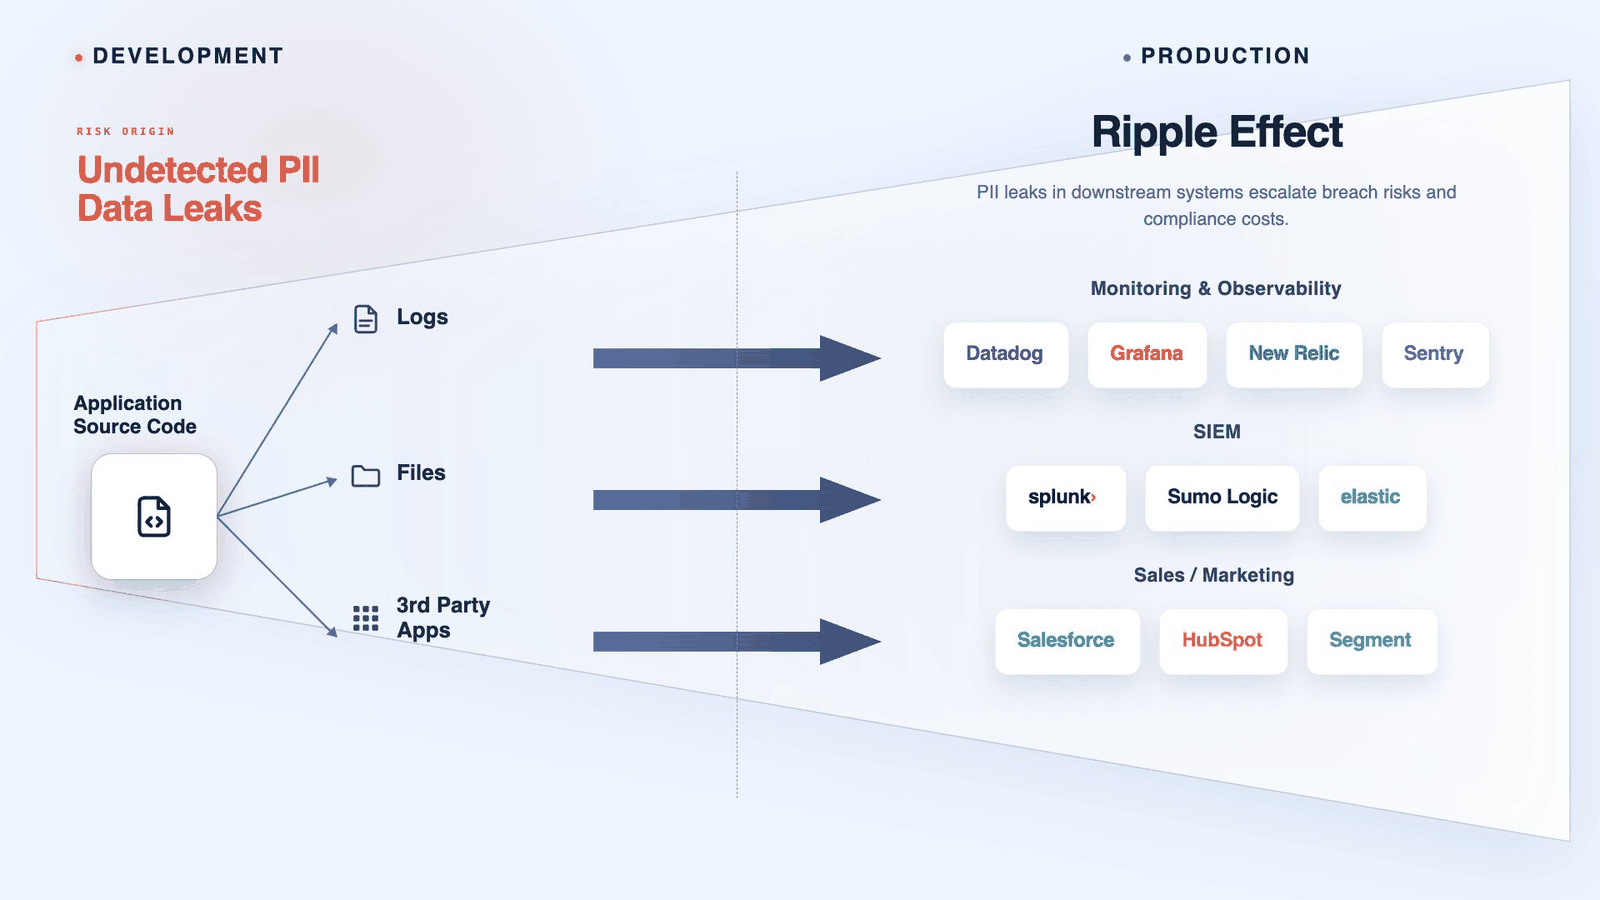
Many organizations know the structured data in their production environments, but undetected PII leaks through logs, files, or third party systems can cascade across systems, raising both the risk and the cost of mitigation. Most companies depend on data security and DLP platforms that only respond once data has entered production, which adds risk, complexity, and cost. Privacy has to start in code, before the data ever flows.
Challenges in Privacy Compliance
GDPR compliant processing activity records are crucial but hard to keep, because data maps fall behind product development. Privacy teams frequently find themselves caught off guard by new product features that process personal data in non compliant ways.
The Limitations of SAST Scanners
One might expect SAST scanners to catch these PII leaks before code is merged and pushed to production, but today's SAST scanners cannot detect sensitive data flows, for several reasons. Pattern matching rules work well when patterns are predictable (for example, an insecure gRPC connection using grpc.WithInsecure()), but they struggle with code that handles sensitive data like social security numbers, where developers may name the functions and methods involved in many ways. And to map data flows across an entire codebase, SAST scanners would have to connect the dots across multiple files and data sinks, which they struggle to do. Solving that requires a scanner built for sensitive data from the ground up.
Introducing HoundDog.ai: An AI Powered Privacy Code Scanner to Stop PII Leaks at the Source and Automate Data Mapping for GDPR Compliance
The HoundDog.ai Privacy Code Scanner addresses these challenges with AI and an extensive library of finely tuned definitions for sensitive data, encompassing most PII, PIFI, and PHI data types. Unlike current SAST scanners, the AI workflow was built in from the beginning, not bolted on after the fact. The scanner uses advanced code analysis to enhance true positive detection and map data flows, including interprocedural analysis and taint analysis to identify manipulated variables across the codebase.
The scanner continuously detects PII leaks that SAST scanners miss: sensitive data exposed in plaintext across mediums such as logs, files, tokens, and cookies, or through third party systems.
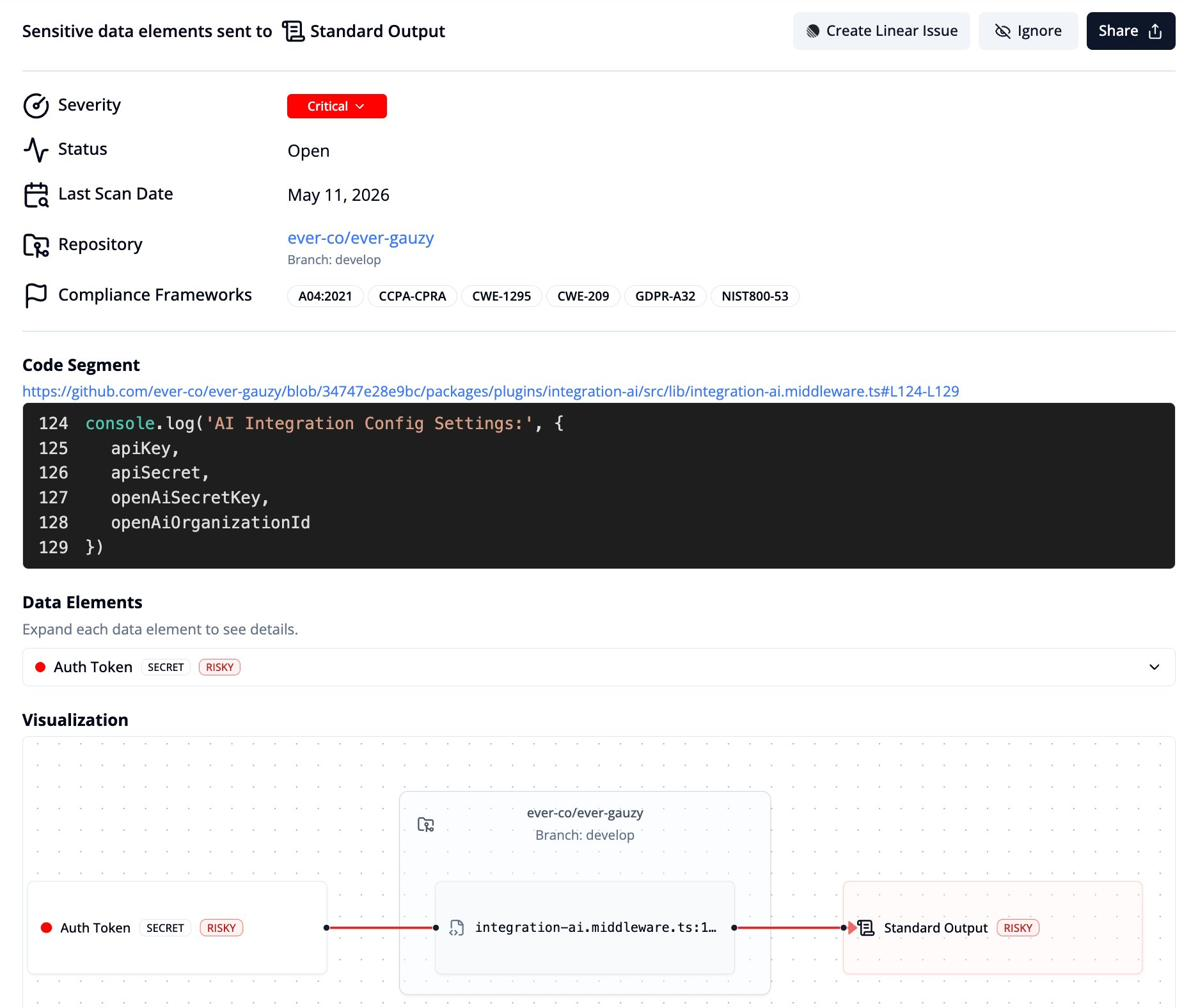
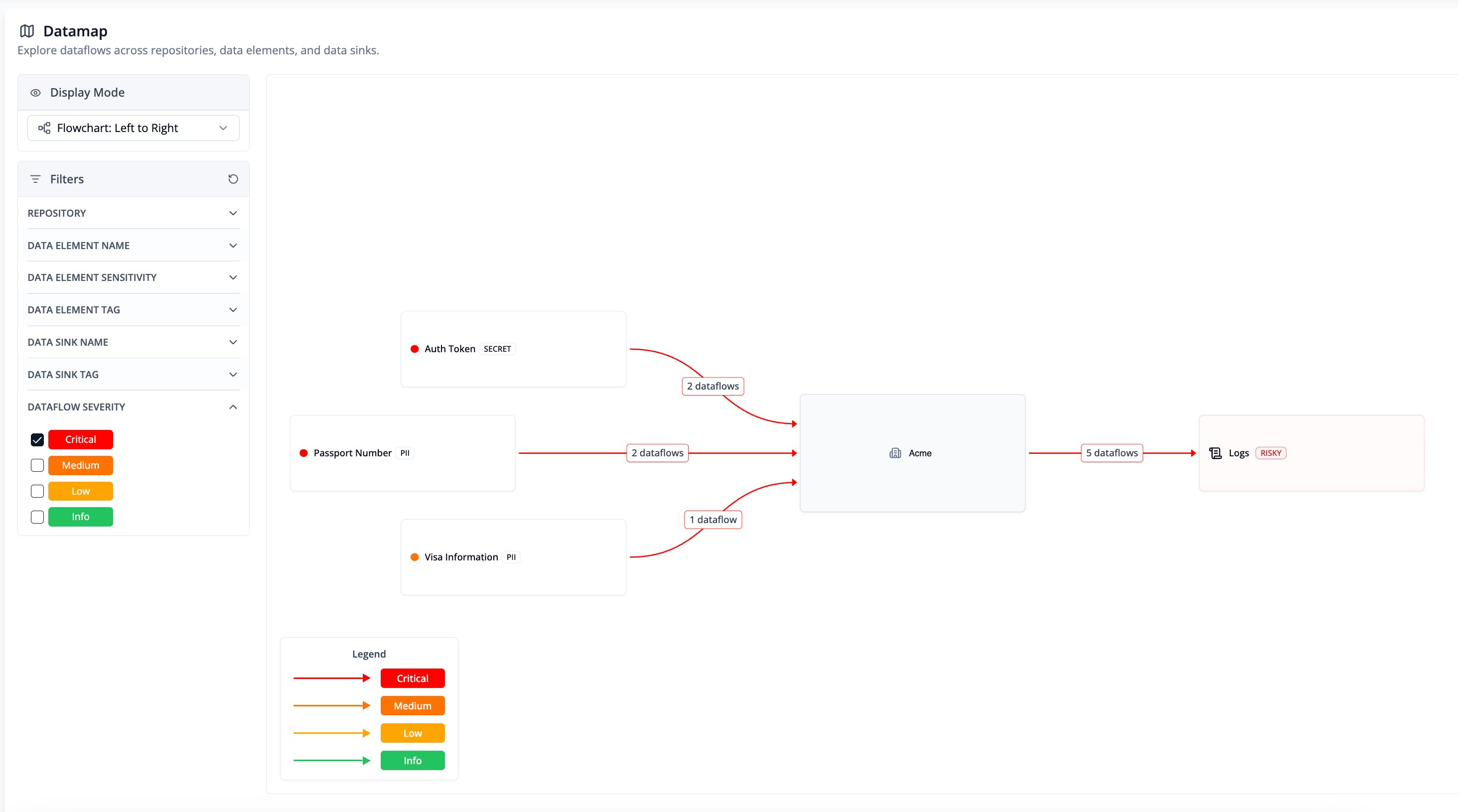
HoundDog.ai also tracks and visualizes the flow of sensitive data, turning what it detects into code level evidence for Records of Processing Activities (RoPA), with privacy teams staying in control of what gets documented. It alerts users when new data elements are introduced, based on their sensitivity levels, so out of scope product changes are caught before they go live. See how it works using our interactive demos.
Fast, Extensible, and Enterprise Ready
HoundDog.ai scans millions of lines of code in under a minute. It supports a wide range of programming languages, integrates with most CI pipelines, and delivers findings directly into GitHub and GitLab security dashboards, with alerts also available through Slack and Jira. The platform is SOC 2 compliant, supports single sign on (SSO), and maintains standardized audit logs.
Try Our Free Scanner
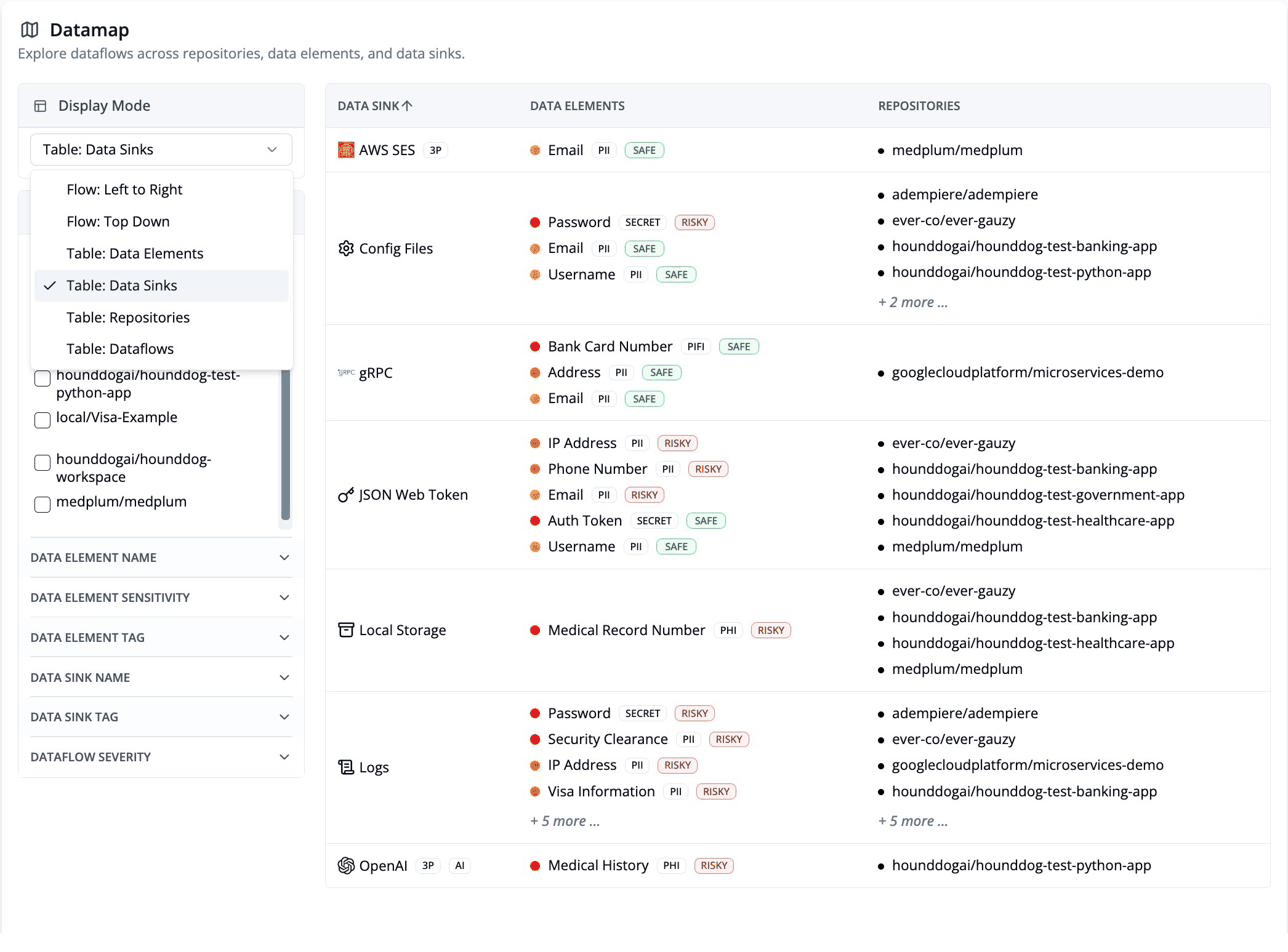
HoundDog.ai offers a free scanner that produces a full data map of sensitive data flows within a codebase, organized by every log, file, token, and third party sink the data reaches. These reports are a critical requirement for documenting processing activities for GDPR compliance, and other security audits need them too. Get started free on GitHub.
We are excited about today's news, and we are already engaged with early access customers who are using HoundDog.ai to solve problems that were intractable before.