Introduction
For government agencies and contractors working toward FedRAMP compliance, an Authority to Operate (ATO) can feel like an uphill battle. The average ATO process takes 6 to 18 months and requires a rigorous System Security Plan (SSP), also called the System Security and Privacy Plan (SSPP), as documented in the FedRAMP reference documentation. Tracking data flows, maintaining PII accountability, and managing third party risks make the ATO process complex and time consuming. This article shows how automating these processes at the code level cuts time and reduces errors, making FedRAMP ATO approval faster.
Eliminating the Headache of Data Flow Mapping (SSP Control: Data Flow Mapping)
The challenge of manual data flow mapping for ATO
Mapping data flows under SSP controls is an essential step toward ATO approval: you need to show exactly how sensitive data is collected, processed, and shared to meet stringent security and privacy standards. Manual data flow mapping is slow, error prone, and built on spreadsheets and documents that quickly go out of date, which leads to delays, missed details, and compliance gaps that put your ATO approval at risk.
How HoundDog.ai helps
The HoundDog.ai Privacy Code Scanner automatically tracks and visualizes how sensitive data, including PII and PHI, flows from your applications into every storage medium and third party integration where it is exposed. Scans run continuously, so your view of all data interactions stays accurate, with no manual mapping and no missed connections. Read more about code level data flow mapping.
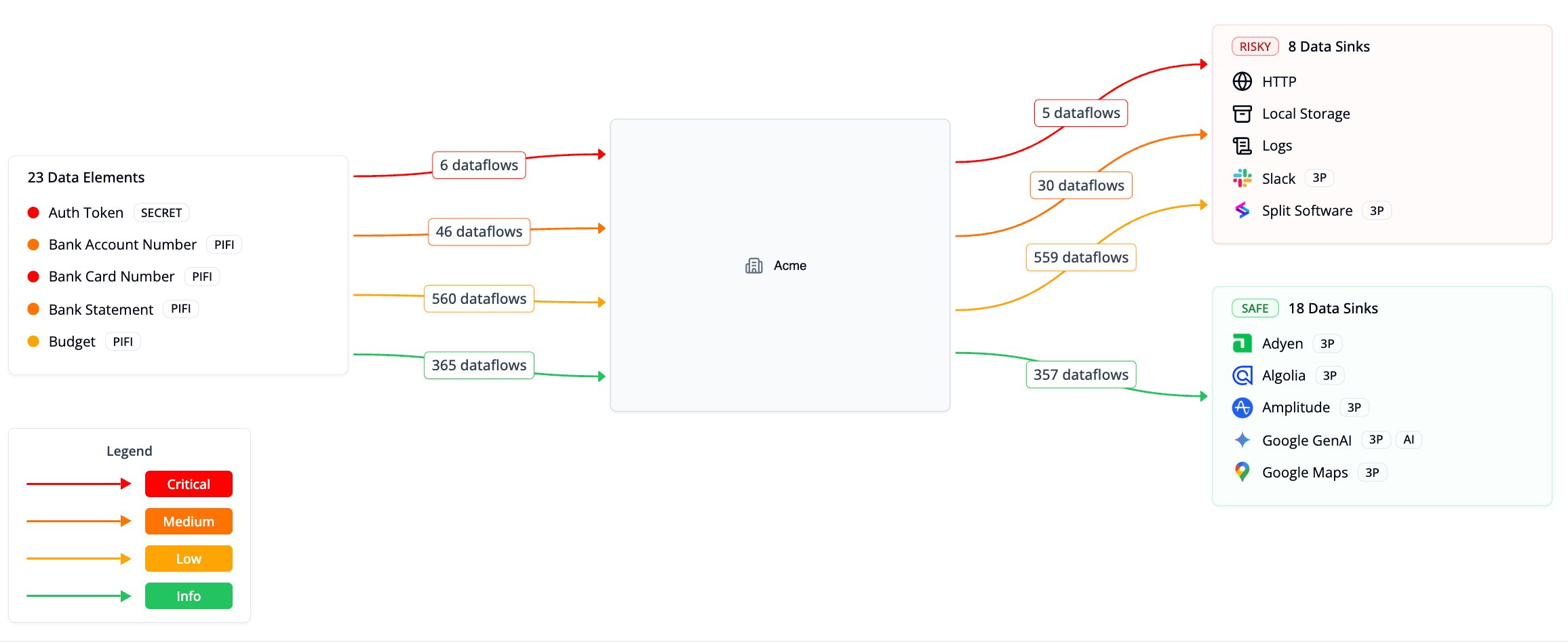
A second challenge is keeping data flow maps current: changes during development create undocumented flows that become compliance risks at audit time. Because scans run on repositories and in CI/CD pipelines, your data flow maps change with the code. An overlooked flow will not catch you off guard in an SSP review, and you can show that your data management practices match what is actually in the code.
Tackling PII Accountability to Meet SSP Standards (SSP Control: Information Management and Accountability)
The difficulty of keeping up with PII management
SSP controls require an up to date, accurate inventory of all personally identifiable information (PII) in your systems: where it is stored, how it flows through your applications, and how it is protected throughout its lifecycle. Many agencies rely on manual processes to track PII, using spreadsheets or static records that quickly fall out of sync. The result is incomplete or inaccurate inventories that stall ATO approvals, invite scrutiny during audits, and consume time that could go to strategic work.
How HoundDog.ai helps
HoundDog.ai automates PII detection across your code repositories. The scanner continuously analyzes source code to see how sensitive data is handled in the codebase itself, without ever accessing production data, logs, or files. That shows where sensitive data appears, which is exactly what SSP information management controls ask you to demonstrate.
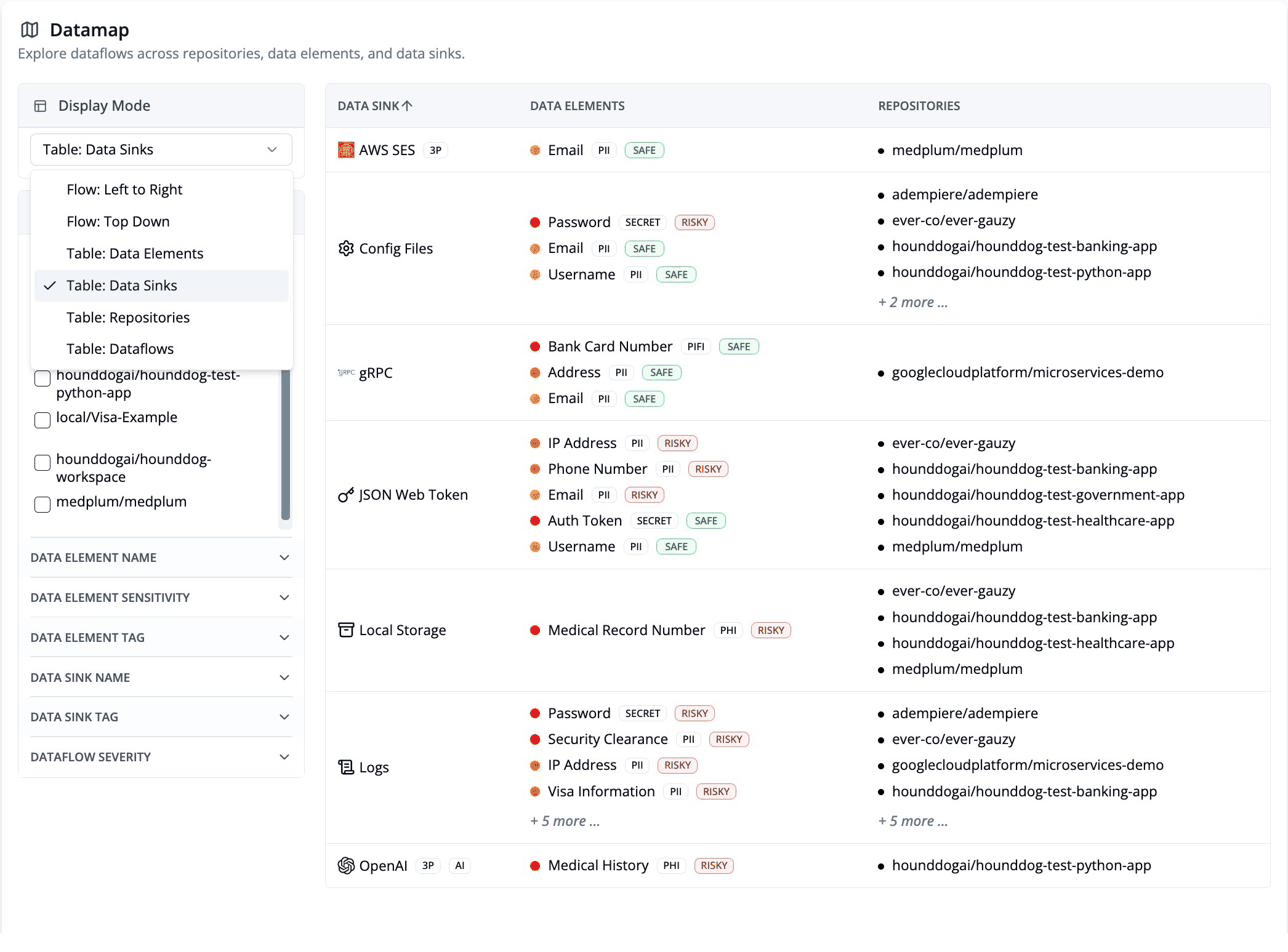
Detection is only half of it. HoundDog.ai also tracks how PII is exposed as development proceeds, closing compliance gaps before they grow. When scans detect new data flows or subprocessors, they are surfaced as suggested edits to your organization's Records of Processing Activities, with your privacy team reviewing and approving each update. Your documentation stays current and evidence backed, without a last minute scramble to update records or explain discrepancies during an SSP audit.
Managing Third Party Risk to Prevent Compliance Failures (SSP Control: Third Party Risk Management)
The challenge of third party oversight in the ATO process
Third party risk management is an important part of SSP controls and of the ATO process. When your systems rely on third party services, you need confidence that those integrations meet your security and privacy standards. Monitoring third party processors is difficult, especially when data sharing risks surface late in development, forcing costly last minute adjustments and compliance issues that slow down ATO approval.
How HoundDog.ai helps
HoundDog.ai monitors every third party interaction visible in your source code. It checks data flows against your Data Processing Agreements (DPAs) and flags potential violations before code reaches production, replacing time consuming and error prone manual audits of third party data handling. Your team learns about privacy and security risks early in the development cycle and can address them while staying aligned with SSP third party risk monitoring expectations.
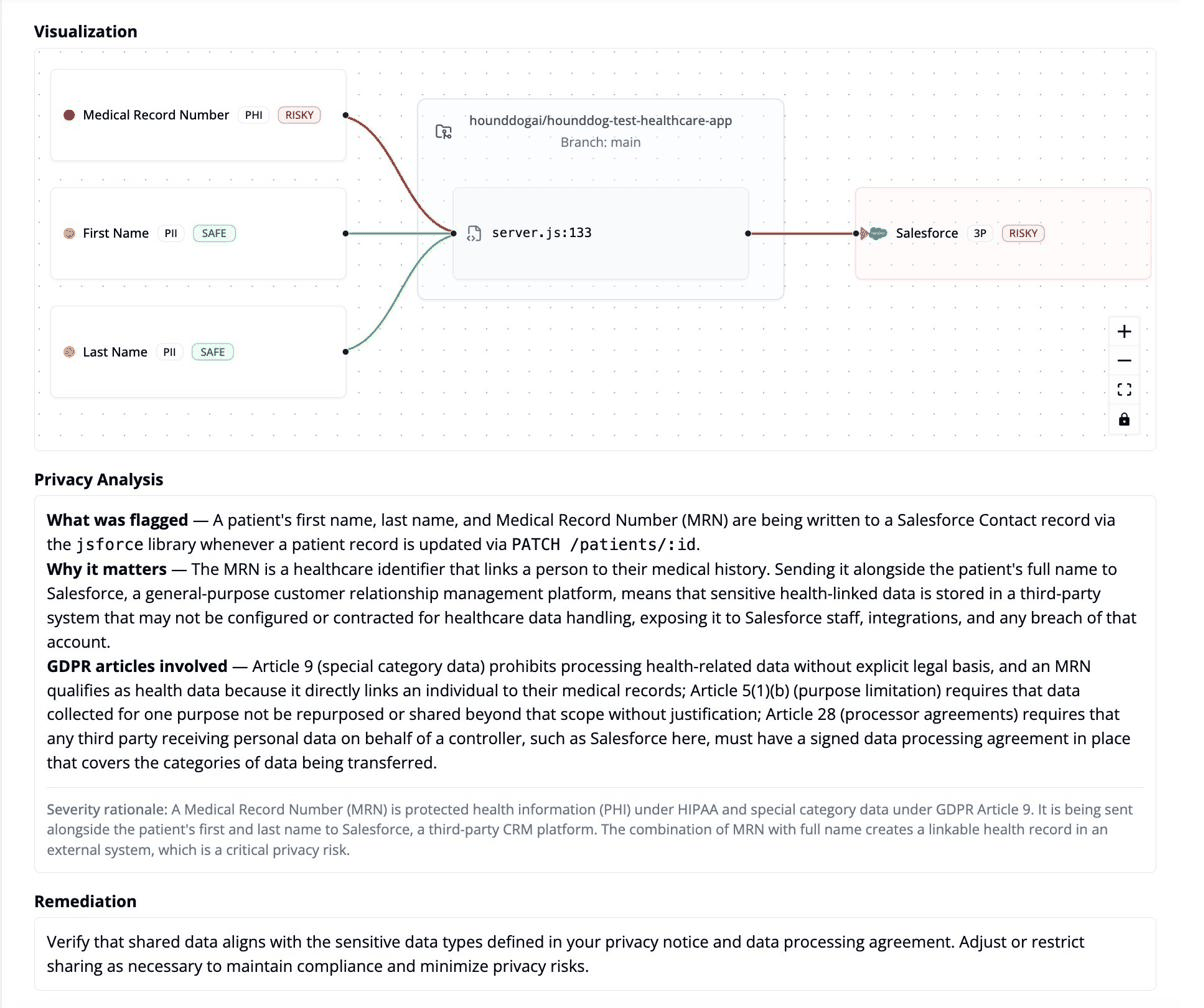
Catching these risks early also prevents expensive remediation. Post production compliance failures rarely mean just a fix; they disrupt the entire ATO timeline and take resources to correct. Addressing third party issues during development keeps your approval on schedule.
Toward Continuous ATO
Agencies are increasingly moving from point in time authorization toward continuous ATO (cATO), where the evidence behind the authorization is regenerated as the system changes rather than reassembled every audit cycle. That model only works if the underlying artifacts, data flow maps, PII inventories, and third party records update themselves at development speed.
Code level scanning fits this model: every commit refreshes the data flow map, every newly introduced data element or integration is flagged for review, and processing records evolve through approved suggestions instead of annual rewrites. Teams pursuing continuous ATO get a living evidence base; teams on the traditional ATO path get a dramatically shorter assembly job.
Conclusion
The main challenges of the FedRAMP ATO process, manual data flow mapping, outdated PII management, and third party risk oversight, are all problems of evidence that goes stale faster than teams can refresh it. Automating these processes at the code level keeps documentation accurate and reduces delays on the path to authorization. To simplify your path to ATO approval, book a call with HoundDog.ai, or see how the same approach supports Secure Controls Framework privacy by design alignment.